
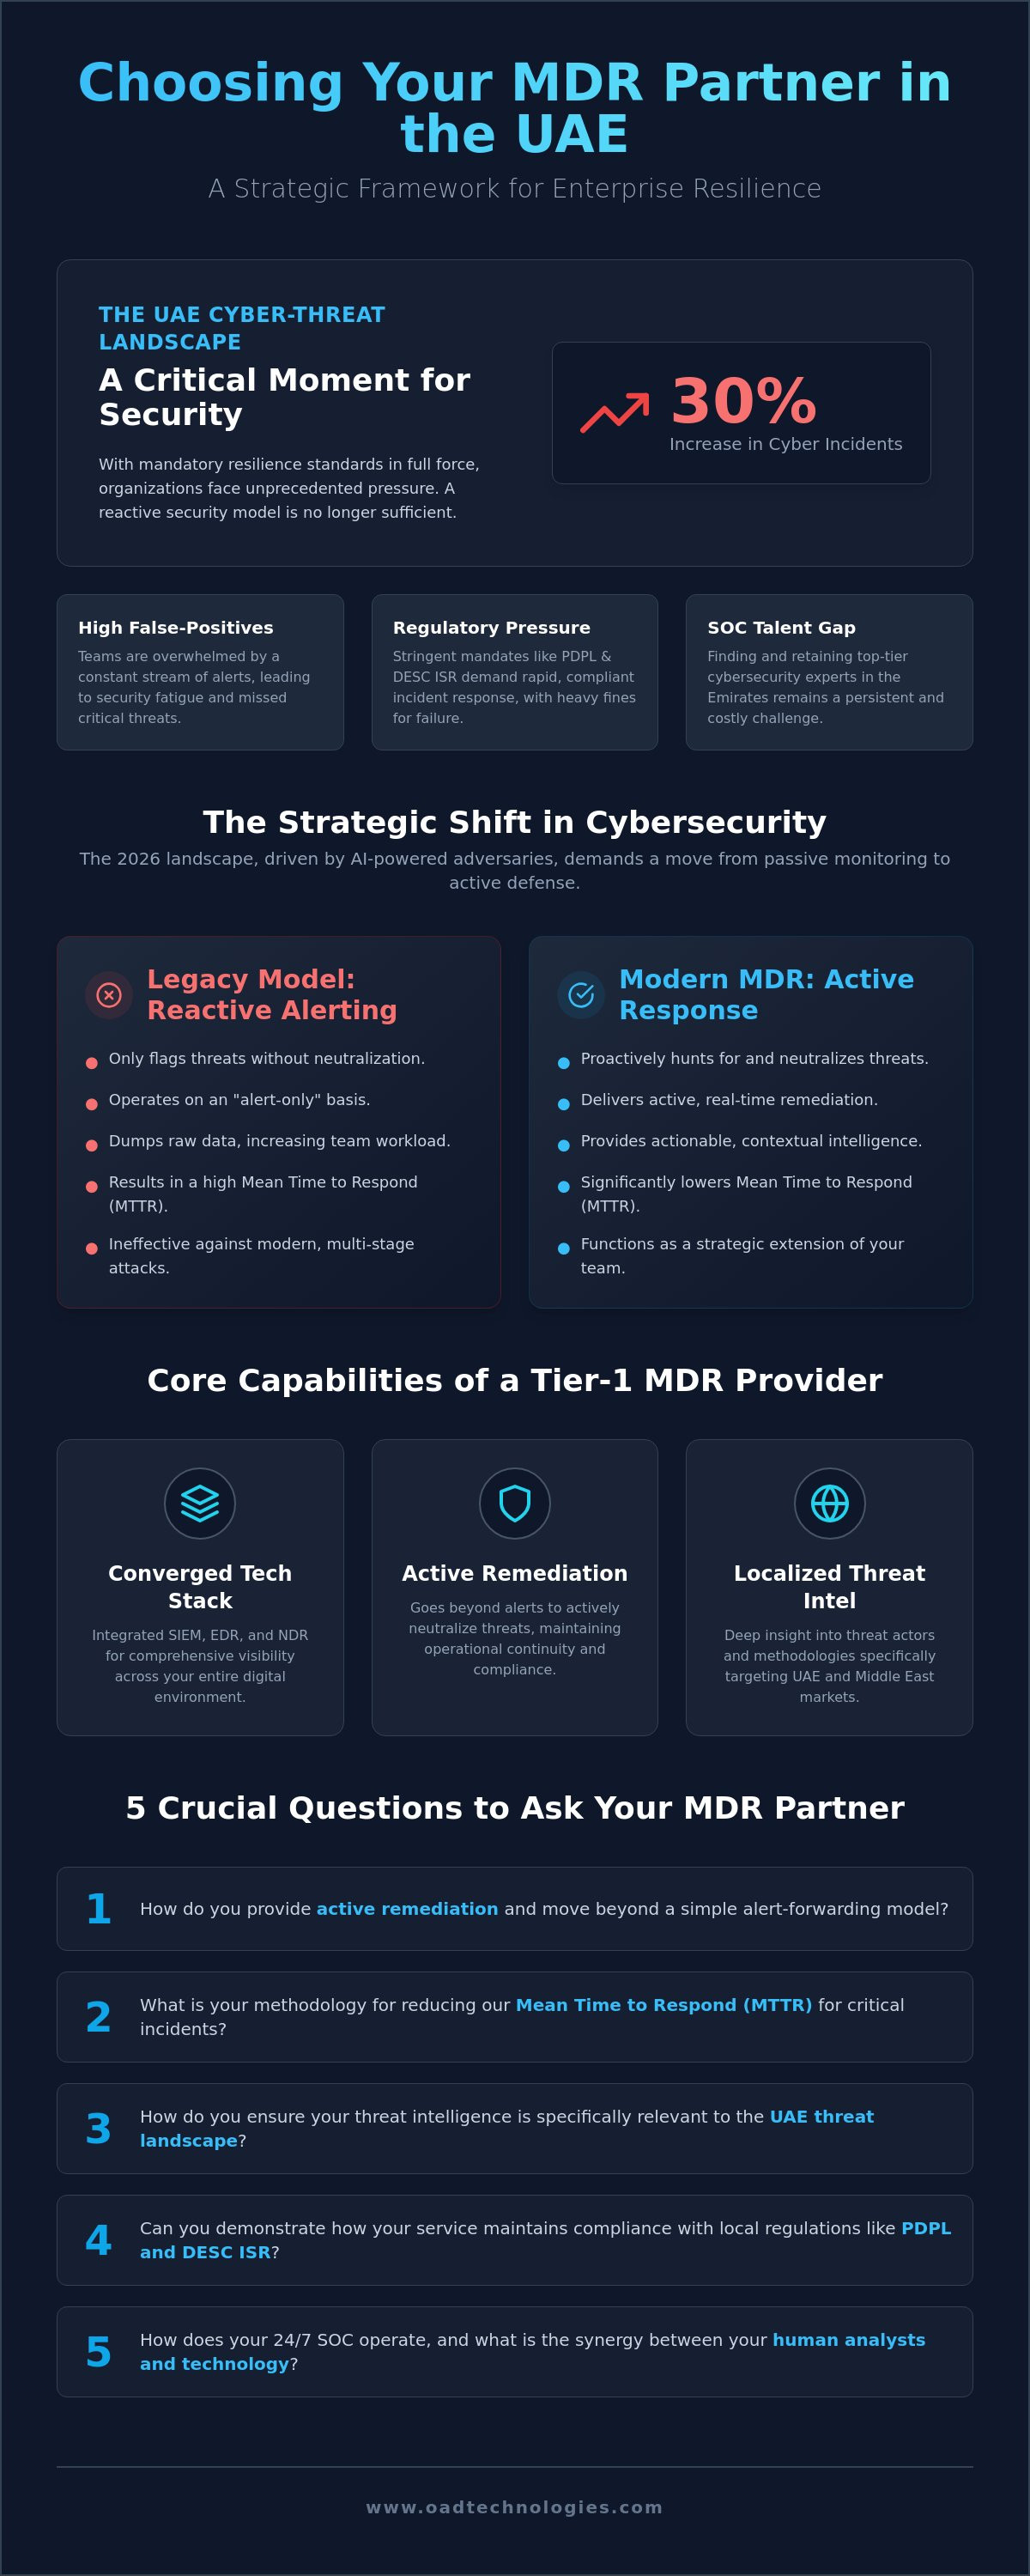
With cyber incidents in the UAE rising by 30% and mandatory resilience standards now in full force, a security model that only flags threats without neutralizing them is a liability. You've likely experienced the fatigue of managing high false-positive rates while your team navigates the complexities of the UAE's stringent regulatory and data protection mandates. It's a significant investment to secure mdr services dubai, yet many organizations still find themselves struggling to bridge the gap between detection and actual response.
We recognize that finding and keeping top-tier SOC talent in the Emirates is a persistent hurdle. This guide, brought to you by OAD Technologies, provides a strategic framework to help you select an MDR provider that functions as a sophisticated extension of your own operations. You'll learn to identify partners who combine technical precision with active remediation and UAE-specific regulatory expertise. We'll outline how to reduce your Mean Time to Respond (MTTR) and build a roadmap for security maturity that ensures your digital assets remain resilient in an evolving market. By prioritizing synergy between human insight and advanced technology, you can finally achieve the 24 X 7 peace of mind your business requires.
Key Takeaways
- Understand the critical shift from reactive monitoring to proactive threat hunting required to counter AI-driven threats in the 2026 landscape.
- Identify the essential technology stack, integrating SIEM, EDR, and NDR, necessary for comprehensive visibility across your entire digital environment.
- Learn why active remediation offers a superior strategic advantage over traditional alert forwarding for maintaining compliance with UAE regulations like DESC ISR and PDPL.
- Master a structured framework for evaluating mdr services dubai to ensure your provider offers localized threat intelligence and transparent operational methodologies.
- Discover how to move beyond off-the-shelf security products toward a customized, "master designer" approach that builds long-term enterprise resilience.
The Evolution of Managed Detection and Response: Why Your Choice of MDR Provider Matters
The cybersecurity paradigm has undergone a fundamental shift. In the 2026 landscape, reactive monitoring is a relic of the past. Organizations can't wait for an alert to trigger; they must engage in continuous, proactive threat hunting. This evolution is driven by the sheer sophistication of AI-powered adversaries that bypass legacy defenses with ease. Traditional antivirus and standalone EDR tools were designed for a different era. They lack the context and the human-led intuition required to neutralize multi-stage attacks before they manifest as breaches. Understanding What is Managed Detection and Response (MDR)? is the first step toward building a resilient architecture.
Modern MDR isn't just a software subscription. It's a strategic entity that bridges the gap between intricate technical telemetry and high-level business outcomes. When evaluating mdr services dubai, it's vital to recognize that your choice of partner dictates your ability to scale without compromising security. A tier-1 MDR provider acts as a strategic partner delivering high-fidelity detection and decisive response to safeguard business continuity.
The 2026 Threat Landscape for UAE Enterprises
The UAE has seen a 30% increase in cyber incidents, with automated ransomware now targeting regional digital assets with surgical precision. These attacks don't just threaten uptime; they put organizations in direct conflict with the UAE Personal Data Protection Law (PDPL). Under these regulations, incident response timelines are non-negotiable. Non-compliance can lead to fines exceeding AED 5 million and significant reputational damage. This high-stakes environment demands a tight integration with your Governance Risk and Compliance (GRC) strategy to ensure every technical action aligns with legal mandates.
Moving Beyond Simple Alert Forwarding
Many legacy providers still operate on an "alert-only" model. They essentially dump raw data into your inbox, leaving your internal team to decipher the noise. In 2026, this approach is unacceptable. The new industry standard is Active Response. This means your partner doesn't just tell you there's a fire; they've already started extinguishing it. At OAD Technologies, we prioritize actionable intelligence over raw data volume. We act as master designers of your security posture, ensuring that mdr services dubai provide real-time remediation that lowers your Mean Time to Respond (MTTR) and protects your long-term digital relevance. By focusing on the synergy between human insight and technological capacity, we empower your team rather than just adding to their workload.
Assessing Core Capabilities: What Defines a Tier-1 MDR Provider?
A tier-1 MDR provider isn't defined by a single tool but by a synchronized ecosystem of technology and human expertise. When evaluating mdr services dubai, you must look for a converged stack that includes SIEM, EDR, and Network Detection and Response (NDR). This trio provides the visibility required to correlate endpoint behavior with network anomalies. This architectural depth is supported by the SANS Institute guide to MDR, which emphasizes that external expertise must optimize your existing infrastructure to be effective. A 24 X 7 Security Operations Centre (SOC) staffed by certified analysts is the heartbeat of this operation, providing the continuous oversight necessary to catch threats in real time.
Threat intelligence is only as valuable as its relevance to your specific environment. A provider must possess deep insight into the threat actors targeting Middle East and UAE markets. Without this regional context, your team will likely drown in alerts that lack business significance. This is where Identity and Access Management (IAM) becomes a critical component of the evaluation. By verifying user context and credential health, MDR analysts can distinguish between a legitimate administrative session and a compromised identity being used for lateral movement.
Detection Fidelity and Proactive Threat Hunting
Signature-based detection is a baseline, not a strategy. Modern adversaries use fileless malware and living-off-the-land techniques that leave no traditional footprint. Advanced mdr services dubai leverage behavioral analysis to identify "silent" indicators of compromise that deviate from established baselines. True MDR providers hunt for threats that have bypassed existing controls, ensuring that stealthy actors don't maintain long-term persistence in your network.
Incident Response and Remediation Maturity
Response maturity is the ultimate differentiator between a vendor and a partner. Most providers stop at simple notification or guided remediation, which still leaves the heavy lifting to your internal team. A master designer of security systems offers Full Active Response, where the SOC takes decisive action to isolate hosts or terminate malicious processes. This requires a delicate balance between automated playbooks and human oversight to prevent business disruption. Integrating findings from Vulnerability Assessment and Penetration Testing (VAPT) allows the SOC to prioritize alerts targeting your most vulnerable assets. If you're looking to elevate your defense, you might explore our strategic approach to active remediation.
MDR Provider vs. Traditional MSSP: Navigating the Strategic Differences
Many organizations in the UAE confuse traditional managed security service providers (MSSPs) with modern MDR. While both offer external support, their objectives differ fundamentally. An MSSP typically focuses on perimeter hygiene, log management, and compliance reporting; they ensure your "digital doors" are locked. In contrast, mdr services dubai assume the adversary is already inside. This threat-focused approach prioritizes identifying and neutralizing active intruders rather than just checking compliance boxes. It represents a critical evolution of SIEM management, transforming a passive repository of logs into a dynamic engine for active defense.
It's common for leadership to question the need for MDR when a managed firewall is already in place. A firewall is a necessary barrier, but it can't respond to a compromised credential or a lateral movement attempt. The most significant differentiator is the Mean Time to Respond (MTTR). Traditional MSSPs often operate on an alert-forwarding model, which creates a delay while your internal team investigates. Modern MDR providers eliminate this lag by executing immediate remediation. This speed is essential in a regional market where a single hour of downtime can result in massive financial and reputational losses.
The Cost of Ownership: In-House SOC vs. MDR
Strategic Synergy: MDR and DLP
Detection is only half the battle; the ultimate goal is the preservation of intellectual property and sensitive resident data. Threat detection through MDR and data protection through Data Loss Prevention (DLP) must work in lockstep to be effective. If an MDR provider identifies a breach but lacks visibility into what data is being exfiltrated, the response is incomplete. OAD Technologies specializes in integrating these two disciplines for national enterprises. We ensure that our active remediation efforts are informed by the sensitivity of the data at risk, providing a holistic shield that maintains your digital relevance and regulatory standing.
Operational Due Diligence: 5 Crucial Questions to Ask Your MDR Partner
Selecting a partner for mdr services dubai is a high-stakes decision that requires more than a review of technical datasheets. You need to verify how a provider operates under pressure and whether their internal culture aligns with your strategic objectives. Transparency is non-negotiable during the due diligence phase. CISOs should specifically ask how the provider handles "Grey Zone" alerts that are suspicious but not clearly malicious to ensure they don't overlook stealthy threats. This level of scrutiny ensures you aren't just buying a tool, but securing a visionary extension of your team.
Question 1: What is your specific response methodology?
Many vendors claim to offer response, but you must distinguish between simple notification and decisive action. Ask for specific examples of "Active Remediation" they have performed for other clients. Do they have the authority to isolate a compromised host or kill a malicious process in real time? Establishing clear "Rules of Engagement" is vital to ensure that active remediation doesn't cause unintended business downtime. Look for a partner who builds customized playbooks tailored to your specific software architecture rather than relying on generic, off-the-shelf scripts.
Question 2: How do you align with UAE-specific regulations?
Local compliance is a moving target in the Emirates. Inquire about their direct experience with Dubai Electronic Security Center (DESC) ISR and NESA standards. Data residency is equally critical under the UAE Personal Data Protection Law (PDPL). You must know exactly where your telemetry is stored and processed to avoid legal complications. Verify their ability to meet the strict incident reporting timelines mandated by regional authorities, as non-compliance can lead to significant financial penalties and loss of government contracts.
Question 3: What is the ratio of human analysts to automated alerts?
Don't let AI buzzwords mask a lack of human expertise. While automation handles the volume, human insight is required for complex investigations and strategic problem-solving. Ask about the certifications of the analysts watching your network, specifically looking for industry-standard credentials like SANS or OSCP. Ensure there is a dedicated technical account manager who understands your business context and can bridge the gap between technical telemetry and executive reporting. If you're ready to move beyond generic security and build a resilient architecture, you can consult with our master designers to evaluate your current posture.
Elevating Enterprise Resilience with OAD Technologies
OAD Technologies understands that enterprise resilience in the UAE isn't achieved through a one-size-fits-all approach. As a premier provider of mdr services dubai, we act as master designers of your security architecture. We don't just deploy off-the-shelf software; we construct customized frameworks that evolve alongside your business. This commitment to strategic partnership ensures your organization remains relevant in an increasingly volatile digital market. By aligning our detection capabilities with Cloud Security Posture Management (CSPM), we provide a unified defense that spans your entire hybrid infrastructure. We focus on long-term viability, positioning ourselves as the guardian of your digital relevance in an ever-changing market.
Our approach rejects standardized, rigid security models. Instead, we favor a structured and logical development of your defense systems. This ensures that your investment in security delivers tangible returns in operational performance. We bridge the gap between high-level innovation and practical business results, ensuring your technology stack isn't just a cost center but a foundation for strategic expansion. Our personality is defined by a proactive, solution-oriented mindset backed by rigorous engineering standards, making us an extension of your own team rather than a distant vendor.
The OAD Advantage: Human Insight + Technological Capacity
Our methodology centers on the synergy between advanced technological capacity and deep human insight. OAD analysts leverage high-fidelity SIEM and EDR telemetry to empower your internal teams, providing the clarity needed to make decisive business decisions. We serve as a guardian for your digital assets, maintaining a proactive stance against regional threat actors. Our holistic suite extends beyond standard monitoring to include critical services like brand protection and VMware replacement solutions. This breadth of capability allows us to address complex digital challenges without resorting to empty marketing clichés. We believe in direct accountability, using an active voice in our remediation efforts to maintain momentum during incident response.
Next Steps for Your Security Transformation
Securing your future starts with a clear understanding of your current security maturity. We invite you to engage in a technical assessment to identify gaps in your existing SOC operations and remediation workflows. Our mdr services dubai are designed for seamless integration with your current network and email security solutions, minimizing friction during deployment. Transitioning to a proactive model shouldn't be a disruption but a strategic upgrade to your operational performance. We have a clear roadmap for every project we undertake, mirroring the structured nature of a well-managed development lifecycle. Consult with an OAD Technologies MDR expert today to begin your transformation into a resilient enterprise.
Securing Your Digital Future through Strategic Partnership
The 2026 threat landscape in the Emirates demands a shift from passive monitoring to active, decisive remediation. We've established that a tier-1 partner must offer more than just alerts; they must provide a customized security architecture that integrates MDR, DLP, and GRC into a single, resilient framework. This alignment ensures your organization doesn't just meet mandatory standards like DESC ISR but actively anticipates and neutralizes sophisticated AI-driven threats. Specialized UAE market expertise is no longer optional. It's the baseline for maintaining business continuity and protecting sensitive data within local borders.
Selecting the right mdr services dubai is a strategic investment in your enterprise's long-term viability. By prioritizing the synergy between human insight and advanced technological capacity, you empower your internal team and gain 24 X 7 peace of mind. OAD Technologies acts as a guardian for your digital assets, offering proactive threat hunting and active remediation playbooks that significantly reduce your Mean Time to Respond. It's time to move beyond off-the-shelf solutions and embrace a master designer approach to your security. Partner with a strategic MDR provider-Contact OAD Technologies today to begin your journey toward lasting digital resilience.
Frequently Asked Questions
What is the difference between an MDR provider and an EDR tool?
EDR is a software category that records and stores endpoint activity, whereas MDR is a managed service that utilizes those tools to hunt for and neutralize threats. Think of EDR as the surveillance camera and MDR as the specialized security team watching the feed and intervening during an incident. While the tool provides the telemetry, the service provides the human expertise and active remediation required to stop an attack.
How does an MDR provider help with UAE ISR and NESA compliance?
MDR providers align with UAE ISR and NESA standards by providing the continuous monitoring and documented incident response evidence required for regulatory audits. These frameworks mandate strict visibility and protection of critical information infrastructure. A managed service fulfills these requirements through detailed logging, rapid remediation reports, and localized threat intelligence that matches regional compliance mandates.
Can an MDR provider replace my existing internal security team?
An MDR provider doesn't replace your internal security team; it empowers them by removing the burden of 24 X 7 alert management. This partnership allows your staff to focus on high-level digital strategy and business-aligned security projects while external analysts handle the technical telemetry and threat hunting. It's a collaborative model designed to bridge the gap between human insight and technological capacity.
How much does it typically cost to partner with an MDR provider?
What is the average onboarding time for a managed detection and response service?
Full onboarding for a managed detection and response service generally takes between two to four weeks. This timeline includes deploying sensors across your environment, configuring behavioral baselines, and establishing the specific rules of engagement for your network. A structured onboarding process ensures that the service integrates smoothly with your existing systems without causing operational friction.
How does an MDR provider handle false positives to avoid business disruption?
Analysts filter false positives by utilizing behavioral baselines and human validation before initiating any response actions. This process ensures that legitimate business operations aren't interrupted by "grey zone" alerts that might otherwise trigger automated blocks. By prioritizing high-fidelity detection, the provider ensures that only verified threats are neutralized, maintaining both security and business continuity.
Does an MDR provider monitor cloud environments like Azure or AWS?
Yes, modern mdr services dubai monitor hybrid and multi-cloud environments including Azure, AWS, and local UAE-compliant data centers. This comprehensive visibility is essential for maintaining compliance with the UAE PDPL, which mandates specific data residency and protection standards. Monitoring the entire attack surface ensures that identity-based threats and cloud misconfigurations are identified before they lead to exfiltration.
Disclaimer
Content by OAD Technologies is for general informational purposes only and does not constitute professional or cybersecurity advice. No warranties are made regarding accuracy or completeness; reliance is at your own risk. OAD Technologies shall not be liable for any direct or indirect losses arising from use of this content.