
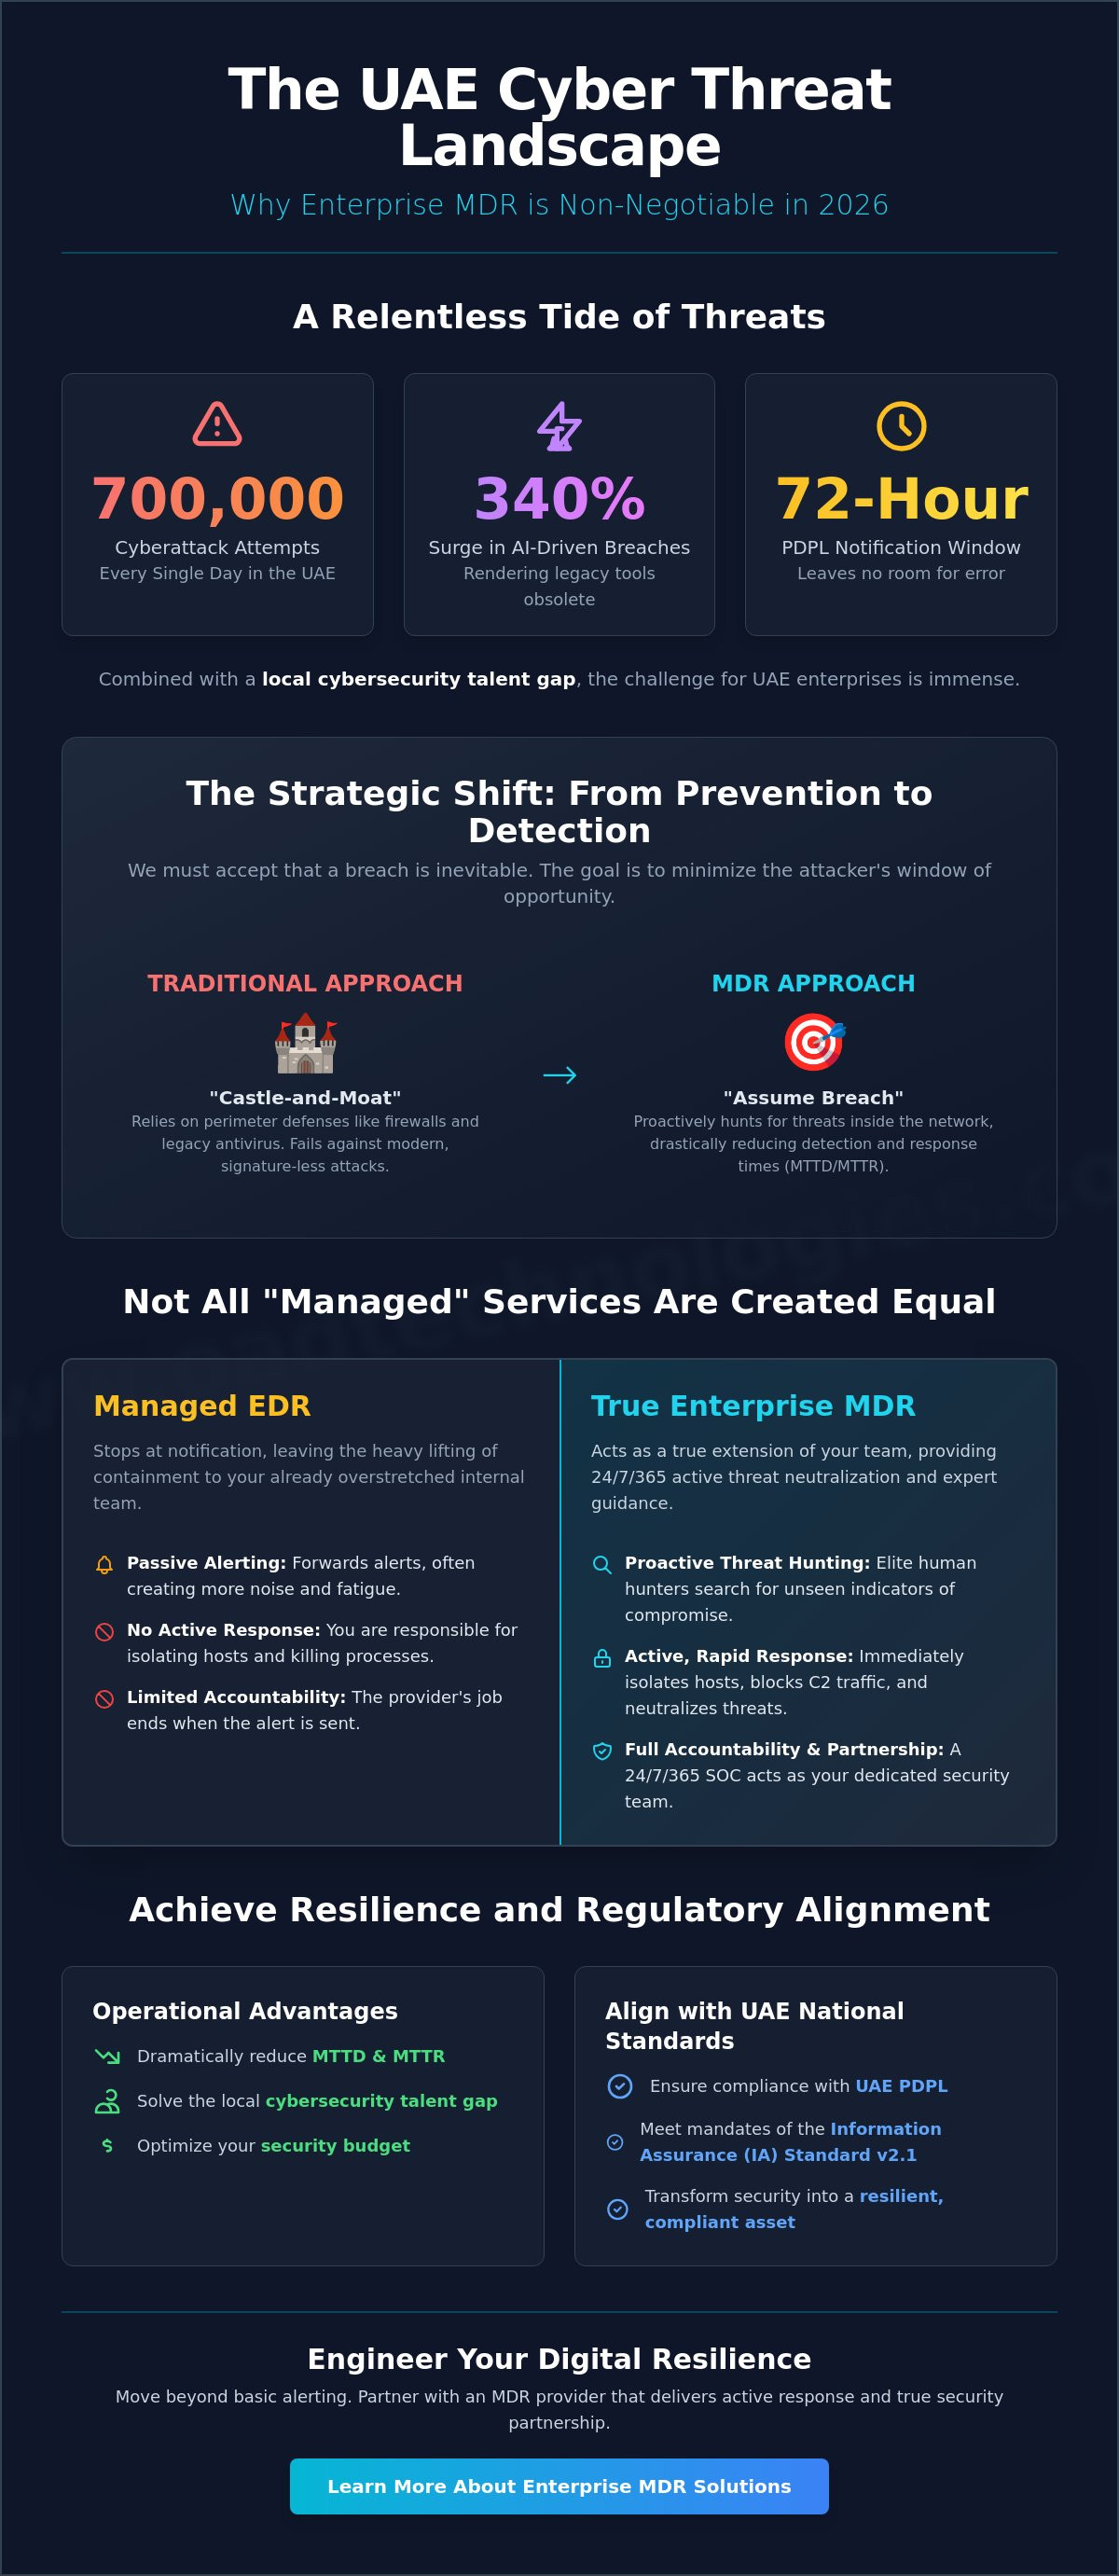
With the UAE facing up to 700,000 cyberattack attempts every single day, your security team is likely battling a relentless tide of noise. It's exhausting to sift through a mountain of false positives while trying to maintain compliance with the UAE Information Assurance Standard v2.1. You know that traditional defenses aren't enough to stop AI-driven breaches, which surged by 340% in early 2026. Implementing robust enterprise mdr solutions uae is no longer just a technical checkbox; it's a fundamental requirement for operational survival.
We understand that hiring elite talent in the local market is a constant struggle, and the 72-hour notification window under the PDPL leaves no room for error. This guide provides a strategic framework to bridge the gap between high-level innovation and practical business results. You'll discover how a synergy of elite human intelligence and proactive technology can reduce your Mean Time to Detect (MTTD) and Respond (MTTR). We'll explore how a tailored MDR partnership transforms your security posture from a reactive cost center into a resilient asset aligned with national standards for 2026.
Key Takeaways
- Understand how intelligence-led MDR addresses the surge in AI-driven ransomware and social engineering targeting the UAE's critical infrastructure.
- Distinguish between basic managed EDR and true MDR to ensure your provider delivers active incident response rather than just passive alerting.
- Evaluate the operational advantages of enterprise mdr solutions uae to solve the local cybersecurity talent gap while optimizing your security budget.
- Align your security framework with UAE national standards, ensuring compliance with the PDPL and the latest Information Assurance (IA) regulations.
- Learn how integrating MDR with Data Loss Prevention (DLP) creates a customized, holistic defense strategy for long-term digital resilience.
The Evolving Threat Landscape for UAE Enterprises in 2026
The UAE's rapid digital transformation has created an expansive attack surface that traditional perimeter defenses can no longer protect. With 700,000 cyberattack attempts recorded daily, the shift from a "castle-and-moat" strategy to a proactive stance is mandatory. Modern Managed Detection and Response (MDR) represents an intelligence-led evolution, moving beyond simple log aggregation to active threat hunting. For organizations seeking enterprise mdr solutions uae, the focus has moved from blocking known signatures to identifying the subtle behavioral anomalies that indicate a sophisticated breach in progress.
By 2026, the primary threat vector has evolved into a blend of targeted ransomware and AI-driven social engineering. Attackers now use machine learning to automate reconnaissance and craft deepfake content that bypasses traditional email filters. These signature-less attacks render legacy antivirus software obsolete because they don't rely on known file hashes. National enterprises require a framework that doesn't just wait for an alert but actively seeks out adversaries hiding within the network. This requires a synergy between automated analytics and human intuition to separate genuine threats from the background noise of a complex digital estate.
The Rise of Advanced Persistent Threats (APTs) in the Region
APTs are designed to be quiet and persistent. They bypass standard firewalls by exploiting zero-day vulnerabilities or using stolen credentials obtained through sophisticated phishing. In the Middle East, geopolitical tensions drive state-sponsored activities targeting critical infrastructure and financial hubs. These actors don't just want to disrupt; they want to remain undetected to collect intelligence. In the context of UAE enterprise vulnerability, Advanced Persistent Threats act as invisible residents that bypass traditional security layers to exfiltrate high-value digital assets over extended periods.
Why "Detection" is the New "Prevention"
We must accept the reality that a determined adversary will eventually find a way in. The goal is no longer just "prevention" but minimizing the window of opportunity an attacker has once they've crossed the perimeter. MDR shifts the focus toward containment and mitigation. By maintaining visibility across the entire enterprise estate, from cloud workloads to remote endpoints, we reduce the Mean Time to Detect (MTTD). This strategic shift ensures that a single compromised device doesn't escalate into a nationwide data breach, directly supporting the rigorous 72-hour notification requirements of the UAE PDPL and the security mandates of the IA Standard v2.1.
Defining Enterprise MDR: Beyond Simple Alerting
Many organizations mistake a software license for a security strategy. True maturity in enterprise mdr solutions uae requires a fundamental shift from passive observation to active intervention. While basic managed services might simply forward an alert to your inbox at 3 AM, a mature MDR framework focuses on three non-negotiable pillars: high-fidelity detection, deep forensic investigation, and rapid, automated response. This transition is critical for maintaining alignment with UAE Information Assurance (IA) standards, which demand more than just a paper-based compliance posture.
The marketplace is often clouded by "Managed EDR" offerings that masquerade as full MDR. The difference lies in accountability. Managed EDR typically stops at notification, leaving the heavy lifting of containment to your already overstretched internal team. In contrast, "True MDR" provides active response. This means that when a threat is identified, the service provider has the authority and technical capability to isolate the affected host, kill malicious processes, and block command-and-control traffic immediately. This engine is fueled by rich telemetry from both Endpoint Detection and Response (EDR) and SIEM platforms, ensuring that no siloed data point is ignored. Effective security requires 24 X 7/365 coverage by a specialized Security Operations Centre (SOC) that acts as an extension of your business, not just a distant vendor.
Proactive Threat Hunting vs. Reactive Monitoring
Elite human hunters don't wait for an alarm to go off. They search for the "unseen" indicators of compromise (IoCs) that automated tools might miss. By using behavioral analytics, these specialists identify subtle deviations from your enterprise's established baseline. This synergy between human insight and technological capacity is what defines a modern defense. It's about finding the adversary during the reconnaissance phase, long before they can execute a payload. If you're looking to evolve your current setup, you might consider how customized security architectures empower your team to stay ahead of these threats.
Incident Response and Remediation Capabilities
The first sixty minutes of a cyber attack, often called "The Golden Hour," determine the ultimate cost of the breach. During this window, MDR specialists deploy remote containment strategies to isolate infected endpoints, effectively halting lateral movement across your network. This isn't just about stopping the fire; it's about guided remediation. We provide specific, actionable steps to harden the environment and ensure long-term system growth, preventing the same vulnerability from being exploited twice. This level of precision ensures that your digital evolution remains uninterrupted by the chaos of a security crisis.
MDR vs. Traditional SOC: Navigating the Strategic Shift
Building an in-house Security Operations Centre (SOC) was once the gold standard for large-scale security. However, the financial and operational burden of maintaining such a facility has become unsustainable for many national entities. When evaluating enterprise mdr solutions uae, decision makers must look beyond the technology stack to the actual business outcomes. A traditional SOC often results in alert fatigue, where internal teams are buried under thousands of low-fidelity notifications. MDR replaces this noise with actionable intelligence. It's the difference between being told there's a fire and having a specialized team already on-site with an extinguisher.
The "talent gap" in the UAE has reached a critical point. Hiring and retaining a 24 X 7/365 team of elite cybersecurity analysts is increasingly difficult and expensive. Competition for skilled professionals in Abu Dhabi and Dubai is fierce, leading to high turnover rates that disrupt security continuity. By shifting to an MDR model, organizations bypass the recruitment cycle entirely. You gain immediate access to a mature, high-functioning team that acts as a strategic partner. This shift ensures your security posture remains resilient without the constant overhead of training and re-hiring internal specialists.
Cost-Benefit Analysis for UAE Decision Makers
The total cost of ownership (TCO) for a private SOC includes massive capital expenditure (CapEx) for hardware, SIEM licenses, and physical security. These costs are often front-loaded and require frequent refreshes to stay relevant. In contrast, MDR operates on a predictable operational performance model. You trade unpredictable overheads for a streamlined subscription that scales with your business. While an in-house SOC demands significant upfront investment in infrastructure and personnel, an MDR model provides a high-velocity return on investment by delivering immediate, expert-led protection from day one.
Operational Synergy: How MDR Empowers Internal Teams
Aligning MDR with UAE Regulatory Compliance (PDPL & ISR)
Compliance in the UAE has evolved from a static goal into a high-stakes operational mandate. With the enforcement of Federal Decree-Law No. 45 of 2021 (PDPL) and the recent UAE IA Standard v2.1 issued in November 2025, the margin for error has vanished. For organizations deploying enterprise mdr solutions uae, the primary objective is ensuring that the strict 72-hour breach notification window is met with forensic precision. Without real-time detection and automated reporting, providing the UAE Data Office with accurate impact assessments within three days is nearly impossible.
This regulatory pressure makes MDR a core component of a modern Governance, Risk, and Compliance (GRC) strategy. Continuous monitoring doesn't just stop threats; it creates a verifiable record of security posture. By maintaining detailed telemetry and incident logs, enterprises can demonstrate due diligence to national regulators. This is particularly vital for entities handling critical services where compliance with the Dubai Information Security Regulation (ISR) is mandatory. To ensure your infrastructure meets these rigorous national standards, explore our compliance-ready security services today.
Meeting National Information Security Regulation (ISR) Standards
MDR provides the mandatory audit trails required for Dubai government entities and private companies handling government data. These standards require more than just a firewall; they demand a documented history of incident response. By aligning threat detection with national risk management frameworks, MDR ensures that every anomaly is investigated and categorized. This systematic approach allows for reporting timelines that satisfy both the ISR and broader federal requirements, turning security logs into a strategic asset for regulatory audits.
Data Sovereignty and Local Security Operations
Data residency is a non-negotiable requirement for many UAE enterprises. Using purely offshore MDR providers carries the risk that sensitive security logs and metadata might leave national borders, potentially violating local data sovereignty laws. We understand that local jurisdiction matters. A provider with a deep understanding of the UAE legal landscape ensures that your data remains protected under the correct legal framework. This commitment to local security operations offers the promise of long-term viability, positioning your organization as a guardian of national digital relevance.
OAD Technologies: Engineering Resilient MDR Partnerships
At OAD Technologies, we reject the standardized, one-size-fits-all approach that defines much of the cybersecurity market. We believe that enterprise mdr solutions uae must be as unique as the organizations they protect. Our role is that of a master designer, crafting bespoke security architectures that bridge the gap between high-level innovation and practical business results. By treating security as a continuous engineering project rather than a static purchase, we ensure your defense evolves alongside your digital ambitions. We don't just provide a service; we act as a guardian of your ongoing digital relevance.
The OAD difference lies in our ability to create a holistic protective shield. We don't view MDR in isolation. Instead, we integrate it with Data Loss Prevention (DLP) to ensure that even if a perimeter is breached, your most sensitive data assets remain unreachable. We also leverage our findings from Vulnerability Assessment and Penetration Testing (VAPT) to feed real-world intelligence back into the MDR engine. If our VAPT team discovers a potential entry point during a technical assessment, our MDR analysts immediately refine detection rules to monitor that specific vector. This creates a closed loop of proactive defense that traditional vendors simply can't match.
Strategic Integration of MDR, EDR, and SIEM
A unified security fabric is built on the precise integration of EDR, SIEM, and MDR telemetry. Our commitment to high-quality craftsmanship means we don't just dump data into a dashboard. We curate it. We empower your internal team through tools that provide clarity rather than just more noise. This synergy between human insight and technological capacity allows your specialists to make informed decisions based on a single, verified version of the truth. We focus on precision, ensuring that every alert is investigated with the technical authority your enterprise deserves.
A Roadmap for Ongoing Digital Relevance
Our partnerships are built for the long term. As the 2026 threat landscape shifts toward more autonomous and decentralized attacks, your security posture must adapt. We provide a clear roadmap that moves from initial implementation to a state of ongoing resilience. This ensures your organization doesn't just keep pace with the market but actively shapes its own digital future. We're here to solve complex digital challenges with grounded, visionary strategies. Consult with OAD Technologies to design your enterprise MDR framework and secure your long-term viability in an ever-changing market.
Securing Your Digital Future in the UAE
The transition toward intelligence-led security is no longer optional. By 2026, the complexity of the threat landscape and the rigor of UAE regulations like the PDPL demand a more sophisticated approach than traditional SOC models can provide. Moving beyond simple alerting to active, human-led response creates a resilient foundation for system growth. Selecting the right enterprise mdr solutions uae allows your organization to turn compliance from a burden into a competitive advantage while solving the local talent gap through strategic partnership.
True digital resilience requires a master designer who understands the synergy between technology and human insight. OAD Technologies offers UAE-based security operations expertise and a specialized integration of DLP, SIEM, and EDR. This ensures your security fabric is customized for your specific operational needs and remains fully aligned with national ISR standards. It's time to move past daily firefighting and focus on your strategic expansion. Partner with OAD Technologies for Enterprise MDR Excellence and ensure your organization remains protected and relevant in an ever-changing market. We're ready to help you build a safer tomorrow.
Frequently Asked Questions
What is the difference between MSSP and MDR in the UAE market?
MSSPs primarily focus on managing security infrastructure and generating alerts based on known signatures. MDR goes further by utilizing elite human intelligence to hunt for unknown threats and execute immediate containment actions. For organizations evaluating enterprise mdr solutions uae, the distinction lies in the shift from passive tool management to active, intelligence-led defense that prioritizes outcomes over simple log aggregation.
How does MDR help with UAE Personal Data Protection Law (PDPL) compliance?
MDR provides the real-time visibility needed to satisfy the strict 72-hour notification requirement under the UAE Personal Data Protection Law (PDPL). By maintaining detailed forensic logs and automated reporting, enterprises can quickly assess the impact of a breach. This proactive approach ensures that data controllers can provide the UAE Data Office with accurate information during a security event, reducing the risk of non-compliance penalties.
Can MDR replace our existing internal security team?
MDR is designed to empower, not replace, your existing security professionals. It acts as a collaborative extension of your team, taking over the burden of 24 X 7 monitoring and low-level alert triage. This allows your internal staff to focus on high-level strategy and the long-term digital evolution of your business while specialized analysts handle the technical complexities of threat hunting and rapid response.
What is the typical onboarding time for an enterprise MDR solution?
The onboarding timeline for a comprehensive enterprise mdr solutions uae deployment typically ranges from four to twelve weeks. This period involves a structured phase of environment discovery, integration of telemetry sources like EDR and SIEM, and the baseline analysis of your network traffic. We ensure that detection rules are meticulously tuned to your specific operational environment before moving to full active response mode.
Does MDR include active incident response or just notifications?
True MDR must include active incident response. Unlike basic managed services that only notify you of a potential threat, our analysts have the authority to isolate compromised endpoints and block malicious traffic in real-time. This immediate intervention stops lateral movement during the critical "Golden Hour" of an attack, significantly reducing the potential damage to your enterprise assets and ensuring faster recovery times.
How does OAD Technologies handle data residency for security logs?
We address data residency by utilizing localized infrastructure and ensuring that sensitive security metadata remains within the UAE's jurisdiction. This approach is essential for meeting the requirements of the UAE IA Standard v2.1 and the Dubai ISR. By keeping logs within national borders, we help you avoid the legal risks associated with offshore data processing and maintain full compliance with national sovereignty mandates.
What telemetry sources are required for effective MDR?
Mature MDR relies on a broad spectrum of telemetry, including endpoint data, network logs, and identity management signals. We also integrate cloud security posture data and email security logs to create a unified security fabric. This multi-layered visibility ensures that our human hunters can identify subtle anomalies across your entire digital estate, from on-premise servers to remote workstations and mobile devices.
Is MDR suitable for enterprises with multi-cloud environments?
MDR is ideally suited for enterprises operating across multi-cloud and hybrid environments. Our framework provides consistent security visibility across platforms like Azure and AWS, ensuring that your security posture doesn't become fragmented. This centralized approach allows for the same rigorous detection and response standards to be applied to all your cloud-native workloads, ensuring that your strategic expansion remains protected regardless of where your data resides.
Disclaimer
Content by OAD Technologies is for general informational purposes only and does not constitute professional or cybersecurity advice. No warranties are made regarding accuracy or completeness; reliance is at your own risk. OAD Technologies shall not be liable for any direct or indirect losses arising from use of this content.


