
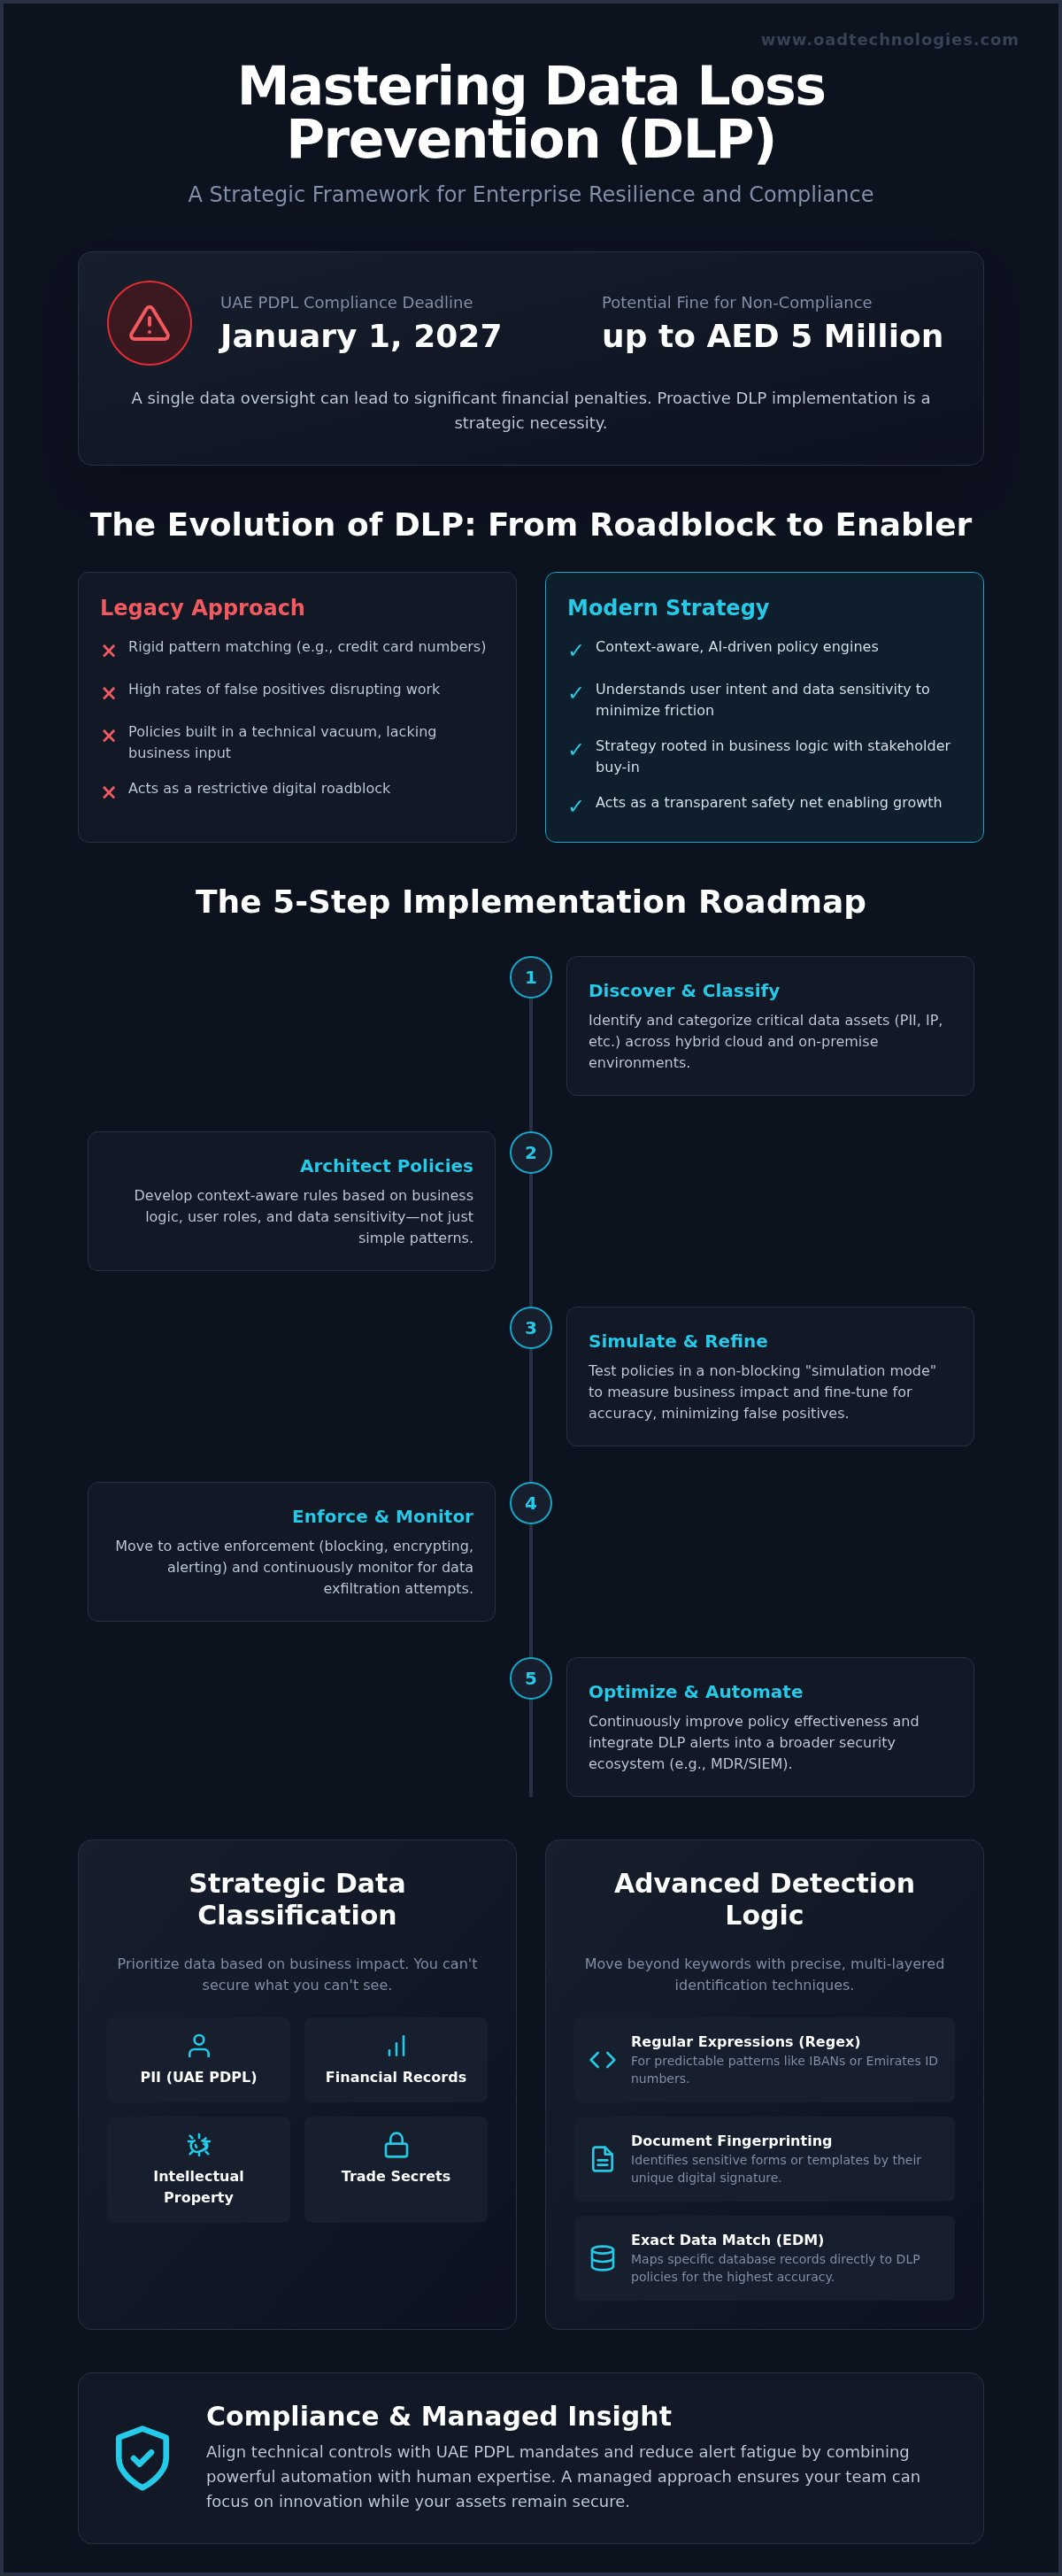
With the January 1, 2027, deadline for UAE PDPL compliance approaching, a single data oversight could cost your organization up to AED 5 million in fines. Mastering dlp implementation best practices is no longer just a technical requirement; it's a strategic necessity for any enterprise operating in the region. You've likely struggled with high false-positive rates that disrupt your operations or found it difficult to map technical policies to strict national regulations. Classifying unstructured data across hybrid clouds remains a complex hurdle that many teams fail to clear.
We believe that true data security isn't about rigid blocking but about creating a sophisticated, resilient architecture. This guide provides a strategic framework to help you align your security posture with both business goals and regulatory mandates. You'll discover how to move from fragmented tools to a phased, visionary approach that secures your assets without causing friction. We'll outline a clear roadmap for policy creation that demonstrates compliance and proactively guards against data exfiltration in an evolving market.
Key Takeaways
- Learn how to evolve your security from legacy pattern matching to context-aware, AI-driven policy engines that minimize operational friction.
- Discover why a phased roadmap moving from data audits to simulation is core to modern dlp implementation best practices.
- Establish a clear hierarchy for identifying and classifying critical assets, including PII and intellectual property, across hybrid cloud infrastructures.
- Ensure strict compliance with UAE PDPL mandates by mapping your technical policies to national data residency and sovereignty standards.
- Understand the benefits of a managed approach that combines automated technical controls with human insight to solve the challenge of alert fatigue.
The Evolution of DLP Policies: Beyond Simple Data Blocking
DLP policies serve as the logic-driven rulesets that govern how your enterprise data moves, who accesses it, and where it resides. In the past, these policies relied on rigid pattern matching, like searching for specific sequences of numbers to identify credit card data. While functional, this legacy approach often results in high false-positive rates that frustrate employees and slow down business. Modern Data Loss Prevention (DLP) has evolved into a sophisticated engine powered by artificial intelligence and machine learning. These engines don't just look for patterns; they understand the intent and sensitivity of the information within its specific environment.
Effective dlp implementation best practices require a shift from purely technical configurations to a strategy rooted in business logic. Many projects fail because policies are built in a vacuum, lacking input from legal, HR, or department heads. Without this stakeholder buy-in, policies often become too restrictive, leading users to find insecure workarounds. By viewing these rules as a core pillar of a comprehensive data loss prevention strategy, you transform security from a digital roadblock into a transparent safety net that protects assets while enabling growth.
The Shift to Context-Aware Data Protection
Modern policy engines leverage metadata and User Behavior Analytics (UBA) to distinguish between a legitimate business process and a potential leak. For example, an employee uploading a large encrypted file to a personal cloud storage account triggers a different response than a financial officer sending a protected report to a verified auditor. You must distinguish between "data in motion" across the network and "data at rest" in storage to apply the right level of scrutiny. Contextual DLP is the precise intersection of content sensitivity, user identity, and the intended destination.
DLP as a Strategic Business Enabler
Well-defined policies do more than just stop leaks; they act as a safeguard for your company's long-term viability. In the UAE, where the PDPL mandates strict oversight, demonstrating robust data controls can lead to reduced cyber insurance premiums and lower legal liability. Protecting intellectual property and trade secrets directly maintains your brand reputation in a competitive market. This approach aligns perfectly with a managed detection and response framework, ensuring that data protection isn't an isolated silo but a synchronized part of your overall security posture. This integration allows your team to focus on innovation while the system handles the complexities of digital asset preservation.
Strategic Policy Architecture: Identification and Classification
Building a resilient defense starts with knowing exactly what you are protecting. You can't secure what you can't see, which makes data identification the cornerstone of dlp implementation best practices. A sophisticated architecture prioritizes data based on its impact on the business. We categorize this hierarchy into four critical tiers: Personal Identifiable Information (PII) governed by UAE PDPL, Financial Records, Intellectual Property, and specific Trade Secrets. While manual classification allows for high precision in small datasets, it lacks the scalability required for a 2026 enterprise. Automation is the only way to maintain pace with the sheer volume of data generated across hybrid environments.
To move beyond simple keyword searches, your policy engine must utilize advanced detection logic. Regular Expressions (Regex) handle predictable patterns like IBANs or Emirates ID numbers. Document Fingerprinting identifies sensitive forms or templates by their unique digital signature. For the highest level of accuracy, Exact Data Match (EDM) allows you to map specific records from your databases directly to your DLP policies. This technical precision ensures that a leak is identified even if the data is slightly altered or renamed. Integrating these triggers with robust identity and access management ensures that security controls are tied to specific user roles and permissions, creating a multi-layered barrier against unauthorized access.
Data Discovery and Mapping Across Silos
The rise of remote work has led to an explosion of shadow data, which is sensitive information residing in unmanaged cloud buckets or local drives. You must implement continuous discovery tools that scan both on-premises servers and cloud repositories like SharePoint or AWS. Mapping these data flows is essential to identify high-risk egress points, such as unauthorized USB transfers or personal webmail uploads. In the dynamic landscape of 2026, discovery isn't a one-time project but a persistent operational requirement. If you're unsure where your most sensitive data currently sits, our security assessment experts can help map your digital footprint.
The Role of Automated Machine Learning Classification
Unstructured data, such as scanned PDFs or image-based invoices, often bypasses traditional scanners. Machine Learning (ML) fills this gap by analyzing the context and visual structure of files to assign accurate sensitivity labels. These classification tags then act as the primary trigger for enforcement actions, such as automatic encryption or blocking. Maintaining a unified classification schema across your entire security stack ensures that your DLP, EDR, and cloud security tools all speak the same language, providing a cohesive defense that scales with your growth.
The 5-Step Implementation Roadmap: From Simulation to Enforcement
Transitioning from a theoretical architecture to a live environment requires a disciplined, phased approach to avoid operational paralysis. Successful dlp implementation best practices prioritize visibility before control, ensuring that security measures don't inadvertently block legitimate business workflows. This roadmap provides a structured path to move your organization from a state of discovery to one of active, automated protection.
- Step 1: Conduct a Comprehensive Data Audit. Before deploying any rules, you must establish a baseline of normal activity. This involves identifying where your sensitive data lives and how it typically moves across your network.
- Step 2: Deploy Policies in Simulation Mode. Activating policies in a "log-only" state allows you to gather telemetry without impacting user productivity. It's the most effective way to see how your rules would behave in the real world.
- Step 3: Analyze and Refine Policy Logic. Use the data from your simulation to identify false positives. Adjusting your detection thresholds now prevents future friction and ensures your team only investigates high-fidelity alerts.
- Step 4: Enable User Notifications and Policy Tips. Education is a critical layer of defense. By triggering real-time alerts or "Policy Tips" when a user attempts a risky action, you empower employees to make better security decisions.
- Step 5: Transition to Full Enforcement. Once your policies are tuned and your users are educated, you can safely enable blocking for high-risk data movements. This final step seals the gaps in your perimeter and prevents unauthorized exfiltration.
The Simulation Mode Advantage
Deploying in simulation mode provides the empirical evidence needed to prove ROI to executive leadership before a single file is blocked. It often reveals "broken" business processes where employees use insecure shortcuts simply because the official method is too cumbersome. By identifying these gaps early, you can fix the underlying process rather than just treating the symptom. Simulation mode is for risk mapping, not just testing. This phase allows you to visualize the potential impact of your security posture on every department, from finance to research and development.
Policy Fine-Tuning and False Positive Reduction
The difference between a successful deployment and an abandoned one often comes down to the precision of your policy logic. You should adjust proximity requirements, such as ensuring a name and an Emirates ID number appear within 50 characters of each other, to reduce noise. Utilizing siem logs allows you to correlate DLP events with broader security incidents, providing the context needed for rapid response. Exception handling and business justification overrides ensure that high-priority, legitimate tasks can still proceed while maintaining a full audit trail for compliance. This level of granularity is what separates a visionary security strategy from a standard tool configuration.
Compliance Alignment: Mapping DLP to UAE National Standards
The UAE regulatory environment is maturing rapidly, placing a significant legal burden on organizations to safeguard personal data. With the compliance deadline for Federal Decree-Law No. 45 of 2021 (PDPL) set for January 1, 2027, the stakes have never been higher. Non-compliance can lead to administrative fines reaching up to AED 5 million, and unauthorized privacy infringements through technology can even result in detention. Integrating dlp implementation best practices into your core security strategy ensures that these legal mandates aren't just checked boxes but are active technical barriers against data misuse.
Data residency and sovereignty remain top priorities for UAE national entities and government-linked enterprises. Your DLP architecture must be configured to recognize and enforce these boundaries, ensuring that sensitive national data does not exit the country's digital borders without authorization. These policies act as the primary technical controls for your broader governance risk and compliance framework. By maintaining granular audit trails, you provide the transparency required by the UAE Data Office, allowing you to demonstrate exactly how data is accessed, moved, and protected in real-time.
Navigating the UAE Personal Data Protection Law (PDPL)
Mapping your DLP rules to specific PDPL articles is essential for identifying sensitive personal data, such as biometric identifiers or health records. Your policies must explicitly address cross-border transfer restrictions, which are a cornerstone of UAE law. We recommend involving your Data Protection Officer (DPO) in the policy design phase. Their insight ensures that enforcement levels, whether they involve encryption or outright blocking, align with the legal risk appetite of the organization. This collaborative approach transforms DLP from a standalone tool into a legally defensible asset.
Integrating DLP with GRC Frameworks
DLP findings provide a continuous stream of data that should inform your organization's risk register. Instead of relying on annual audits, you can use DLP reporting modules to automate the collection of compliance evidence. To ensure your defenses are truly resilient, we utilize vulnerability assessment and penetration testing to validate that your DLP policies can't be bypassed by sophisticated exfiltration techniques. This rigorous validation confirms that your technical controls match your governance promises. If you need to align your infrastructure with the latest UAE standards, book a GRC consultation with OAD Technologies today.
Managed DLP: Integrating Human Insight with Technical Controls
Deploying a solution is only the first chapter in a much longer narrative of digital resilience. Many UAE enterprises find that even the most robust dlp implementation best practices can falter when faced with the daily reality of alert fatigue and a widening cybersecurity skill gap. Managing a DLP environment in-house often leads to a reactive posture where internal teams are buried under thousands of low-fidelity triggers. This noise doesn't just cause operational friction; it creates dangerous blind spots where genuine threats can go unnoticed. A managed approach transforms this dynamic by providing 24 X 7 monitoring and expert policy tuning that adapts to your evolving business needs.
At OAD Technologies, we don't view DLP as a standalone software installation but as a critical component of a holistic infrastructure protection suite. This perspective ensures that your technical controls are always aligned with your strategic objectives, protecting your most valuable assets without burdening your internal staff. We treat data protection as an evolving lifecycle. As your business grows and your data footprint expands, your policies must be refined to maintain their accuracy and relevance. By integrating human expertise with automated tools, we provide the nuanced analysis required to distinguish between a legitimate business process and a high-risk exfiltration attempt.
Synergy Between DLP, EDR, and Cloud Security
Protecting data at the endpoint requires a seamless integration between EDR and DLP. While EDR monitors for malicious behavior and system compromises, DLP ensures that sensitive information doesn't leave the device through unauthorized channels. This protection extends deep into the cloud, where we utilize cloud security posture management to secure SaaS and IaaS environments. By centralizing policy management across hybrid and multi-cloud architectures, you create a unified defense that leaves no room for shadow data to hide. This synchronized approach ensures that security follows the data, regardless of where it resides or how it's accessed.
Long-Term Resilience through Strategic Partnership
Long-term success in data protection isn't found in a standardized, "set and forget" configuration. It requires the human insight that only a strategic partnership can provide to navigate complex policy decisions that software alone might misinterpret. We help you move beyond reactive blocking toward a proactive model of data stewardship and brand protection. This partnership safeguards your digital relevance and ensures you remain a guardian of your clients' trust in an increasingly complex global market. Contact OAD Technologies for a strategic DLP assessment to begin your journey toward enterprise-grade data resilience.
Future-Proofing Your Enterprise Data Strategy
The shift toward a context-aware security model is no longer optional. It's the foundation of a modern enterprise. By moving beyond rigid blocking and adopting a phased roadmap, you transform security from a cost center into a strategic enabler. Mastering dlp implementation best practices ensures your organization doesn't just meet the January 1, 2027, PDPL deadline but actually strengthens its operational integrity. You've seen how a unified architecture, linking classification with identity and managed detection, creates a resilient barrier against exfiltration.
As a national leader in managed security services, OAD Technologies provides the technical authority and human insight needed to navigate this complex landscape. We are UAE PDPL compliance experts specializing in the strategic integration of DLP with your existing SIEM, EDR, and IAM stacks. Our team acts as an extension of yours, designing customized systems that protect your long-term viability and brand reputation. We bridge the gap between technical innovation and practical business results.
Secure your enterprise assets with a strategic DLP framework from OAD Technologies. Your digital future is built on the strength of the data you protect today.
Frequently Asked Questions
What is the primary difference between a DLP policy and a data backup policy?
DLP focuses on preventing unauthorized data transfer and misuse, whereas backup focuses on data restoration after a loss. DLP is a proactive security measure that monitors data in use, in motion, and at rest to stop leaks in real time. Backup is a reactive recovery tool designed to ensure business continuity after a system failure or ransomware attack. Both are essential, but they serve entirely different roles in an enterprise resilience strategy.
How do DLP policies handle encrypted data or password-protected files?
DLP solutions handle encrypted data by using SSL/TLS inspection to decrypt and scan traffic before it leaves the network. For password-protected files that cannot be inspected, dlp implementation best practices often include policies that block these files by default or require them to be moved through a secure, audited gateway. This ensures that "dark data" doesn't become a blind spot for your security team or a path for exfiltration.
Can DLP policies prevent data exfiltration via physical hardware like USB drives?
Yes, endpoint DLP modules are designed specifically to control physical egress points like USB ports, external drives, and even Bluetooth transfers. You can configure policies to block all unauthorized hardware or allow only company-issued, encrypted devices. This level of control is vital for preventing intentional or accidental data exfiltration by employees or contractors who have physical access to your organization's workstations.
How often should an organization review and update its DLP policy rules?
Organizations should review their DLP rules at least quarterly to account for new data types and changing business processes. However, a more proactive approach involves continuous policy tuning based on the telemetry gathered from your MDR or SIEM integrations. Regular audits ensure that your rules remain effective against evolving threats and stay aligned with the latest UAE ISR requirements and international standards.
What are the most common reasons for high false-positive rates in DLP?
High false-positive rates usually stem from overly broad regular expressions or a lack of business context in policy design. If a rule triggers every time any ten-digit number is detected, it will catch internal phone numbers alongside sensitive identifiers. Using advanced techniques like Exact Data Match (EDM) or document fingerprinting significantly improves accuracy by ensuring the system recognizes the specific, unique structure of your sensitive enterprise assets.
Is it possible to implement DLP policies without impacting remote employee productivity?
You can maintain productivity by using a phased implementation that starts with "Simulation" mode to identify legitimate remote workflows before enforcement begins. Context-aware policies distinguish between a remote developer uploading code to a secure corporate repository and a sensitive file being sent to a personal cloud drive. Providing real-time "Policy Tips" also helps educate employees on secure behavior without halting their work entirely.
How does the UAE Personal Data Protection Law (PDPL) affect DLP policy design?
The UAE PDPL requires specific technical controls for sensitive personal data and mandates strict oversight of cross-border data transfers. Your dlp implementation best practices must include rules that identify data subject to these regulations, such as Emirates ID numbers or biometric records. Failure to align your policies with these national standards can result in significant administrative fines of up to AED 5 million for your organization.
What role does machine learning play in modern DLP policy enforcement?
Machine learning is essential for classifying unstructured data like scanned images, handwritten forms, or complex PDFs that traditional keyword scanners might miss. It also plays a key role in identifying behavioral anomalies, such as an employee suddenly accessing an unusual volume of sensitive files. This intelligence allows the system to move beyond simple "if-then" logic to a more sophisticated, risk-based enforcement model that adapts to user behavior.
Disclaimer
Content by OAD Technologies is for general informational purposes only and does not constitute professional or cybersecurity advice. No warranties are made regarding accuracy or completeness; reliance is at your own risk. OAD Technologies shall not be liable for any direct or indirect losses arising from use of this content.