
A low-cost penetration test is often the most expensive investment a UAE enterprise can make. When you're evaluating the cost of penetration testing in uae, the sticker price rarely reflects the true value of the digital resilience you're actually purchasing. You've likely felt the frustration of receiving opaque quotes that fail to explain how technical vulnerabilities translate into business risk. It's difficult to justify a significant budget to the board when a proposal looks like a generic checklist rather than a strategic defense plan.
We understand that security isn't just about finding bugs; it's about protecting your organization's future in an increasingly complex regulatory environment. This guide provides the clarity you need to move beyond "checkbox" security and build a robust investment strategy. You'll gain a clear understanding of market rates for 2026, from specialized cloud assessments to enterprise-wide red team exercises. We'll also provide a framework to evaluate vendor quality and a roadmap for maintaining long-term digital relevance through the synergy of human insight and advanced technological capacity.
Key Takeaways
- Understand why 2026 marks a shift from commoditized audits to strategic security investments driven by evolving UAE national standards.
- Gain a clear framework for evaluating the cost of penetration testing in uae by balancing technical scope with the value of expert human research.
- Discover why traditional fixed-price models are yielding to more agile solutions like Penetration Testing as a Service (PTaaS) for dynamic cloud environments.
- Learn how to verify a vendor’s technical pedigree using a CISO-approved checklist that aligns with global standards like NIST and OWASP.
- Explore how a precision-engineered approach to VAPT builds long-term digital resilience rather than just satisfying a compliance checkbox.
The Evolution of Cybersecurity Costs in the UAE
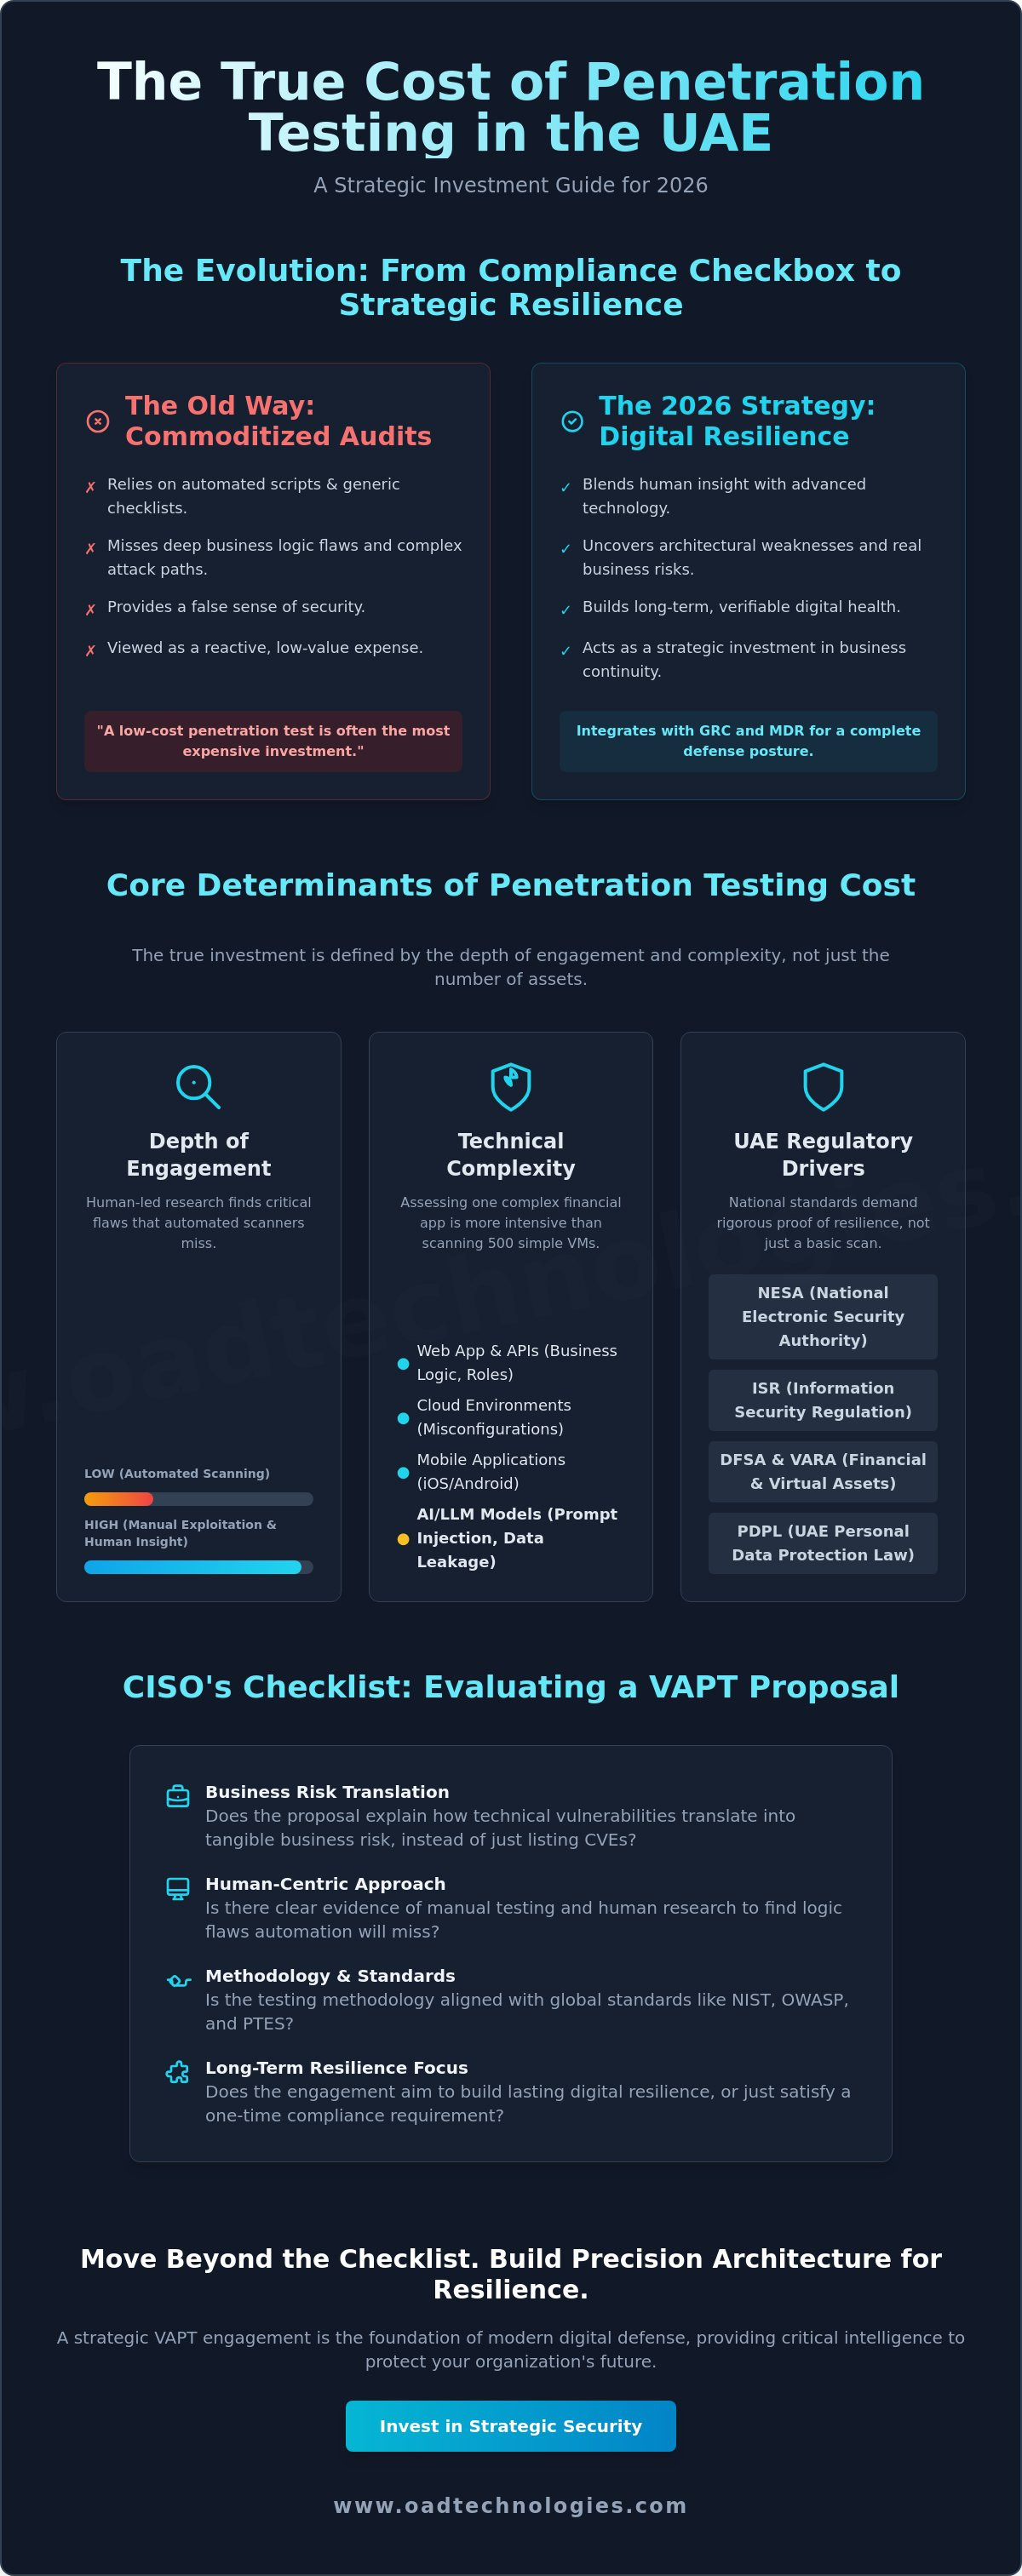
The perception of cybersecurity in the Middle East has undergone a radical transformation. Enterprises no longer view digital defense as a reactive expense; they treat it as a fundamental component of business continuity. The cost of penetration testing in uae reflects this shift toward strategic maturity. In 2026, we're seeing a pivot from periodic, static audits to a model of continuous security validation. This evolution is driven by the emergence of sophisticated threats, such as Agentic AI and vulnerabilities within Large Language Models (LLMs), which traditional scanning tools often miss.
Before diving into numbers, it's vital to clarify the objective. What is a Penetration Test? At its core, it's a simulated cyberattack designed to identify and exploit vulnerabilities in your computer systems. However, in the current UAE market, it's become a diagnostic tool for long-term digital health. The UAE Personal Data Protection Law (PDPL) has established a new baseline for data sovereignty, making regular, rigorous testing a legal necessity for any entity handling sensitive information.
The Regulatory Landscape as a Price Driver
National standards like the National Electronic Security Authority (NESA) and Information Security Regulation (ISR) have redefined testing depth. These frameworks don't just require a scan; they demand proof of resilience. For organizations in specialized sectors, the complexity increases. The Virtual Assets Regulatory Authority (VARA) and the Dubai Financial Services Authority (DFSA) mandate specific, rigorous testing protocols for virtual asset providers and financial institutions. The cost of penetration testing in uae is often a direct reflection of these compliance layers. While a deep VAPT engagement requires a higher initial investment, it's a fraction of the potential fines or the catastrophic fallout of a data breach under modern UAE regulations.
Beyond the Checkbox: Strategic Resilience
Commoditized, "budget" pentests frequently offer a false sense of security. They rely on automated scripts that fail to uncover deep business logic flaws or complex multi-stage attack paths. High-quality testing provides the architectural insight needed to build a truly resilient system. This process works best when integrated into a comprehensive governance risk and compliance framework. By identifying weaknesses before they're exploited, VAPT serves as the critical intelligence feed for your managed detection and response strategy, ensuring your team knows exactly where the perimeter is most likely to break.
Core Determinants of Penetration Testing Cost
Calculating the cost of penetration testing in uae requires moving past the "Scope Paradox." Many procurement teams mistakenly believe that asset volume is the primary price driver. In reality, testing 500 identical virtual machines is often less resource-intensive than assessing a single, high-stakes financial application with complex business logic. The true investment is defined by the depth of engagement and the level of manual exploitation required to mirror a determined adversary. A simple IP count doesn't capture the hours needed to bypass modern security controls or test intricate user permission structures.
Automation has its place in a modern security stack, but it can't replace human architectural insight. While automated scanners identify known CVEs, they lack the curiosity to chain minor misconfigurations into a full system compromise. High-tier researchers spend hours understanding your unique software architecture to find flaws that logic-blind algorithms miss. This human-centric approach is what transforms a standard audit into a strategic defense mechanism. If you're looking for precision in your security architecture, exploring specialized VAPT solutions ensures your investment targets actual risk rather than just theoretical vulnerabilities.
Technical Complexity and Asset Volume
The architecture of your digital estate dictates the testing rigor. Assessing a web application involves more than checking for SQL injection. It requires evaluating user roles, session management, and the resilience of API endpoints. As enterprises integrate AI, specialized testing for Large Language Models (LLMs) has become a premium requirement in 2026. These assessments target prompt injection and data leakage, which are far more complex than legacy network scans. Additionally, integrating NIST Risk Assessment Framework principles ensures that Cloud Security Posture Management (CSPM) is evaluated alongside traditional infrastructure to capture the full risk profile of hybrid environments.
Methodology and Certification Standards
Methodology significantly impacts the final cost of penetration testing in uae. A black-box test, where the researcher has zero prior knowledge, requires more time for initial reconnaissance. Conversely, white-box testing provides full access to source code and documentation, allowing for a deeper, more efficient analysis of the internal logic. The technical pedigree of the team also matters. CREST-certified testers command a higher rate because they've demonstrated a rigorous standard of ethics and technical proficiency. In a high-stakes national environment like the UAE, the necessity of manual exploitation cannot be overstated. It's the difference between a report that lists potential issues and one that provides a validated, technical remediation roadmap.
UAE Market Pricing Models: Fixed-Price vs. Strategic Engagement
Predictability is a comfort, but in cybersecurity, it's often a trap. While fixed-price models offer a clean line item for procurement, they struggle to accommodate the fluid nature of modern cloud environments. If your infrastructure evolves weekly, a static assessment scope quickly loses relevance. We're seeing a fundamental shift in how the cost of penetration testing in uae is structured, moving away from rigid contracts toward more adaptive, strategic engagements that prioritize actual risk over arbitrary asset counts.
Penetration Testing as a Service (PTaaS) has emerged as a preferred model for UAE enterprises seeking continuous validation. Unlike traditional one-off audits, PTaaS provides an ongoing stream of intelligence that matches the pace of your development lifecycle. For high-stakes adversary simulations, time-and-materials models often yield a higher return on investment. They empower researchers to pursue complex attack paths to their logical conclusion, ensuring that no sophisticated threat remains hidden behind a scope boundary. This flexibility is essential for identifying the chained vulnerabilities that automated tools consistently miss.
Low-bid proposals frequently come with hidden financial anchors. It's common to see budget vendors charge extra for retesting vulnerabilities after remediation or for providing the reporting depth required for board-level presentations. These administrative add-ons, combined with potential travel and reporting fees, can quickly push the total cost of penetration testing in uae beyond the original quote. A strategic partnership prioritizes transparency, ensuring the initial price reflects the full lifecycle of the engagement, including follow-up support and technical guidance.
Comparative Pricing for Common Engagements
- External Network Perimeter Testing: Market rates in May 2026 typically range from AED 35,000 to AED 75,000, depending on the volume of live assets and service complexity.
- Internal Network and Active Directory Assessments: Pricing is driven by infrastructure size and domain complexity. These tests often cost 10 to 30 percent more than external assessments due to the depth of internal reconnaissance required.
- Enterprise Red Team Exercises: These comprehensive simulations range from AED 250,000 to over AED 1.5 million, reflecting the months of specialized manual exploitation required to test your full defensive posture.
The Long-term Viability of Strategic Partnership
Building a relationship with a dedicated security partner creates a compounding value effect. Over time, your partner gains a deep understanding of your architectural nuances, which reduces the technical overhead of subsequent tests. This synergy allows for a more focused defense, especially when integrating VAPT results with a robust identity and access management framework. By combining human intuition with automated threat detection, you ensure your security posture remains resilient against both known and emerging threats, securing your digital relevance in a volatile market.
Evaluating a VAPT Proposal: A CISO’s Checklist
Selecting a cybersecurity partner involves more than a simple price comparison. When you evaluate the cost of penetration testing in uae, you must look beyond the bottom line to the technical pedigree of the researchers involved. A high-quality proposal should explicitly name the engagement leads and provide a summary of their regional experience. In the UAE's specific regulatory environment, having a team that understands local compliance mandates is essential. Avoid firms that utilize senior staff for the sales process only to delegate the actual testing to junior analysts who lack architectural depth.
Transparency in methodology is another non-negotiable factor. Your chosen partner must align their testing protocols with globally recognized frameworks such as NIST, OWASP, and PTES. This alignment ensures that the assessment is rigorous, reproducible, and capable of satisfying both internal stakeholders and external regulators. Furthermore, a comprehensive proposal must include a clear remediation roadmap and a dedicated retesting phase. Without a structured follow-up, a penetration test is merely a snapshot of failure rather than a catalyst for improvement. To ensure your next assessment meets these rigorous standards, consult with our precision architecture team today.
Red Flags in Low-Cost Pentesting Quotes
Low-cost quotes often mask significant security risks. If a vendor promises "automated VAPT," they are offering a contradiction in terms. Automation is excellent for identifying known vulnerabilities, but it cannot simulate the creative, multi-stage attack paths used by modern adversaries. Standardized, one-size-fits-all approaches are dangerous because they ignore your organization's unique business logic. These "checkbox" audits provide a false sense of security while leaving critical vulnerabilities exposed to exploitation.
Maximizing Value from Your Security Assessment
Efficiency begins with internal preparation. You can significantly reduce billable hours and lower the overall cost of penetration testing in uae by providing your testing team with updated network diagrams, API documentation, and clear access credentials before the engagement begins. This allows researchers to spend their time on manual exploitation rather than basic reconnaissance. Use the resulting intelligence to drive your data loss prevention initiatives, ensuring that your most sensitive data assets are protected by verified controls. The ROI of deep-dive testing is the delta between the manageable cost of proactive discovery and the catastrophic economic impact of a reactive breach response.
The OAD Technologies Approach: Precision Architecture for Resilience
OAD Technologies rejects the notion that security can be bought off a shelf. Standardized, commodity assessments often fail because they treat every enterprise network like a generic template. When you're calculating the cost of penetration testing in uae, the real value lies in the bespoke nature of the engagement. We act as master designers of systems, ensuring that our vulnerability assessment and penetration testing pillars are customized to your specific software architecture. This approach bridges the gap between visionary innovation and the practical, grounded results your board expects.
Our methodology focuses on precision and high-quality craftsmanship. We don't just hand over a list of vulnerabilities; we provide a strategic roadmap for long-term digital relevance. By avoiding generic buzzwords and focusing on industry-standard professional terminology, we speak effectively to both executive leadership and technical specialists. This balance ensures that the technology we deploy is always framed within a clear business context, focusing on investment returns and operational performance.
Integrated Defense: From VAPT to DLP
A penetration test shouldn't exist in a vacuum. Most traditional vendors treat assessments as standalone tasks, but we view them as a critical diagnostic for your entire security ecosystem. Our findings directly inform and strengthen your Data Loss Prevention (DLP) posture by identifying exactly where sensitive data is most at risk. We also integrate these insights with your SIEM to ensure that identified weaknesses are monitored with high-fidelity alerts. This creates a feedback loop where human-led threat hunting and automated detection work in tandem. It's a proactive mindset that transforms a one-time assessment into a continuous shield for your digital assets.
Your Roadmap to National Cybersecurity Leadership
Achieving national cybersecurity leadership in the UAE requires moving beyond simple compliance. It's about active threat mitigation and long-term viability. We treat every client's system as a unique digital asset, applying rigorous engineering standards to every engagement. This commitment ensures that your organization doesn't just meet current regulations but is prepared for the threat landscape of 2026 and beyond. By focusing on strategic expansion, we position ourselves as guardians of your ongoing digital relevance. The true cost of penetration testing in uae is an investment in your company’s future stability. Partner with OAD Technologies for a strategic security assessment to build a foundation of precision-engineered resilience.
Architecting Your Path to Digital Resilience
The landscape of 2026 demands a shift in perspective. Viewing cybersecurity as a static line item is no longer viable for UAE enterprises navigating complex NESA and PDPL mandates. You've seen how the true cost of penetration testing in uae is measured not just in AED, but in the depth of technical expertise and the long-term protection of your digital assets. By moving beyond commoditized scans and prioritizing human-led research, you transform a compliance necessity into a strategic advantage.
At OAD Technologies, we bridge the gap between high-level innovation and practical business results. Our approach centers on the sophisticated synergy between human intuition and AI-driven tools, ensuring your defenses are as dynamic as the threats they face. We specialize in integrating VAPT findings into broader Data Loss Prevention (DLP) frameworks, providing a roadmap that secures your ongoing digital relevance. Don't settle for a checkbox audit when you can build a foundation of precision-engineered security.
Request a Strategic VAPT Consultation with OAD Technologies to align your security investment with your long-term business goals. We're ready to act as an extension of your team, helping you master the complexities of the modern threat landscape with confidence and clarity.
Frequently Asked Questions
How much does a basic penetration test cost in the UAE in 2026?
A basic web application penetration test in 2026 typically starts around AED 7,000 for limited scopes, while more comprehensive assessments for complex applications can reach AED 55,000. These entry-level figures represent engagements that satisfy foundational compliance needs. The final price depends heavily on the depth of manual exploitation required to move beyond simple automated scanning.
Why is there such a large price range for VAPT services in the region?
The wide price range is driven by the depth of testing, technical complexity, and the specific expertise of the researchers involved. A standard scan is far less resource-intensive than a manual, deep-dive assessment that targets intricate business logic flaws. The cost of penetration testing in uae scales based on the number of user roles, API endpoints, and the specific regulatory standards your organization must satisfy.
Does the UAE Personal Data Protection Law (PDPL) require penetration testing?
The UAE Personal Data Protection Law (PDPL) mandates that organizations implement appropriate technical and organizational measures to ensure data security, which necessitates regular security validation. While the law doesn't always use the specific term "penetration testing," it requires proof of effective risk mitigation. Regular VAPT is the industry-standard method for demonstrating this technical compliance to national regulators.
What is the difference between a vulnerability assessment and a penetration test in terms of cost?
Vulnerability assessments are generally less expensive because they rely on automated tools to identify known weaknesses without active exploitation. A penetration test involves a manual effort to exploit those weaknesses, which requires more specialized labor hours. Because of the human expertise involved in the exploitation phase, a pentest can cost significantly more than a simple vulnerability scan.
How often should a UAE-based enterprise conduct a full penetration test?
Most UAE enterprises should conduct a full penetration test at least annually or whenever significant changes occur in their digital infrastructure. Organizations in highly regulated sectors, such as finance or healthcare, often move toward quarterly testing or continuous validation models. This frequency ensures that new vulnerabilities introduced during rapid development cycles are identified before they can be exploited by adversaries.
Are there additional costs for retesting after vulnerabilities are remediated?
Retesting fees vary between providers, with some including a single round of verification in the initial quote while others treat it as an add-on. It's common for vendors to bill for retesting at a discounted daily rate or as a fixed percentage of the original engagement fee. Clarifying these terms during the proposal stage is essential for accurate budgeting and ensuring a clear roadmap for remediation.
Can a small business in the UAE afford professional-grade VAPT?
Small businesses can access professional-grade VAPT by utilizing targeted assessments that focus on their most critical public-facing assets. Many providers offer tiered pricing models that allow smaller entities to meet regulatory baselines without the expense of a full-scale enterprise audit. Investing in a focused assessment helps smaller firms protect their digital relevance while managing the cost of penetration testing in uae effectively.
What drives the cost of a Red Team exercise compared to a standard pentest?
Red Team exercises command a premium because they simulate a full-scale, multi-layered attack over several weeks or months. Unlike a standard pentest that targets specific technical vulnerabilities, a Red Team exercise tests your organization's entire detection and response capability. The increased cost reflects the specialized manual labor, stealth requirements, and the breadth of the simulation across digital and social perimeters.
Disclaimer
Content by OAD Technologies is for general informational purposes only and does not constitute professional or cybersecurity advice. No warranties are made regarding accuracy or completeness; reliance is at your own risk. OAD Technologies shall not be liable for any direct or indirect losses arising from use of this content.


