
What if the ISO 27001 certificate hanging in your lobby is actually a liability rather than an asset? In the UAE's rigorous regulatory climate, "paper-only" compliance is a dangerous gamble that fails the moment a real threat hits your network. Many organizations struggle to map technical controls like DLP and SIEM directly to ISO requirements. This often leaves gaps that lead to failed audits or, worse, data breaches. You're likely looking for iso 27001 certification consultants uae who can move beyond templates to build genuine technical resilience.
This guide provides a roadmap to navigate the complexities of the ISO/IEC 27001:2022 standard while staying aligned with the UAE PDPL. We'll show you how to integrate your security operations, from IAM to MDR, into a cohesive Information Security Management System. You'll learn how to transform compliance from a documentation hurdle into a strategic advantage that protects your brand and ensures a successful certification audit in 2026.
Key Takeaways
- Understand why the ISO/IEC 27001:2022 update and UAE PDPL require a shift from static documentation to active technical enforcement.
- Identify how to select iso 27001 certification consultants uae who possess the technical depth to integrate solutions like SIEM and IAM into your compliance framework.
- Follow a structured 5-phase roadmap that transforms your risk assessment from a paperwork exercise into a core component of your security operations.
- Learn why modern auditors prioritize real-time evidence from tools like MDR and VAPT over traditional policy manuals.
- Build a resilient Information Security Management System that bridges the gap between high-level governance and practical data protection.
The Strategic Importance of ISO 27001 Certification in the UAE
ISO/IEC 27001 represents the international gold standard for Information Security Management Systems (ISMS), offering a structured methodology to manage risks to sensitive corporate data. In the UAE, the year 2026 marks a pivotal turning point. The grace periods for several national data laws have concluded, and the convergence of the UAE Personal Data Protection Law (PDPL) with sector-specific mandates has created a high-stakes environment. Relying on iso 27001 certification consultants uae who understand this local context is no longer a luxury. It's a strategic necessity for any business operating within the Emirates' digital economy.
We've seen a definitive move away from "checkbox compliance." In the past, some firms treated certification as a yearly paperwork exercise. Today, the national market demands continuous security validation. Regulators and partners now look for evidence that your security controls actually work in real-time. This shift mirrors the global trend toward transparency, where a static certificate is less valuable than a living, breathing security posture that adapts to emerging threats.
Alignment with UAE PDPL and National Regulations
ISO 27001 provides the technical skeleton for PDPL compliance. While the law outlines what must be protected, the standard's controls provide the practical "how." For instance, mapping your access controls and encryption protocols directly to the UAE Information Assurance (IA) Standards ensures you meet both international and local benchmarks simultaneously. This integrated approach is critical for organizations navigating the Information Security Regulation (ISR) in Dubai or similar frameworks across the Northern Emirates. ISO 27001 serves as the operational blueprint that transforms abstract UAE GRC requirements into a verifiable and defensible security architecture.
The Business Case for Enterprise Resilience
Resilience is a competitive differentiator. When you bid for UAE government or semi-government contracts, ISO 27001 certification often acts as a pre-qualification shortcut. It proves your organization has undergone rigorous external validation. This status simplifies third-party risk management (TPRM) for international partners, making it easier to facilitate cross-border trade and build trust with global stakeholders.
The financial implications are equally compelling. By implementing proactive risk treatment plans, you mitigate the massive fallout associated with data breaches. In 2026, being "secure enough" isn't a viable strategy. Enterprise resilience is the only way to safeguard your brand and ensure long-term viability in a volatile threat landscape. You aren't just protecting data; you're protecting your company's ability to compete on a global stage.
Decoding the Modern ISMS: Technical Controls vs. Documentation
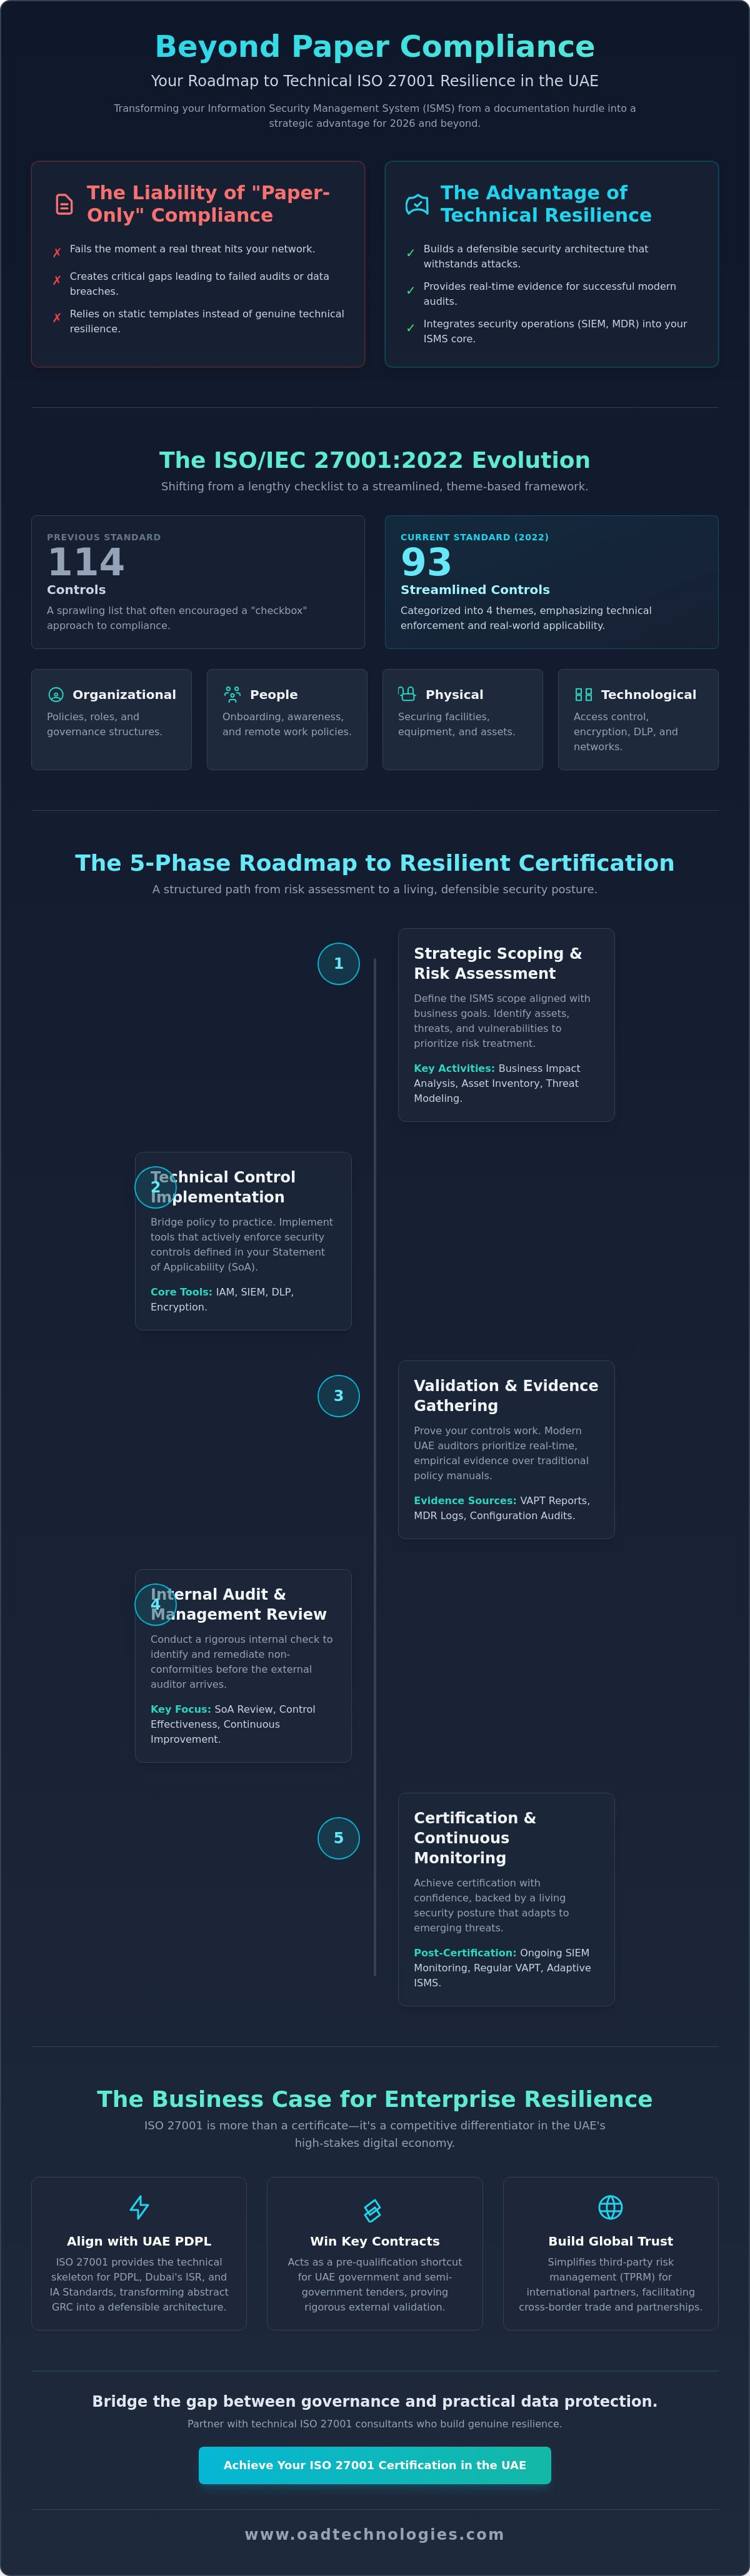
The 2022 update to the ISO 27001 standard fundamentally changed how businesses approach compliance. It moved from a sprawling list of 114 controls to a streamlined set of 93, categorized into four specific themes: Organizational, People, Physical, and Technological. This restructuring isn't just cosmetic. It signals a shift where technical enforcement carries as much weight as corporate policy. Understanding the strategic benefits of ISO 27001 requires looking past the paperwork. Many iso 27001 certification consultants uae still focus on templates, but a modern audit will quickly expose a lack of technical depth.
Policy without enforcement is a major vulnerability. If your manual says "we protect data," but your systems don't actually block unauthorized transfers, the auditor sees a non-conformity. The Statement of Applicability (SoA) acts as your security perimeter's blueprint. It defines which controls apply and how they're implemented. Integrating a VAPT into your risk treatment plan provides the empirical evidence auditors now demand to prove your controls are effective.
Technical Implementation of Annex A Controls
Technological controls are the hardest to fake. Implementing Data Loss Prevention (DLP) ensures that sensitive UAE resident data doesn't leave your control. Similarly, Identity and Access Management (IAM) fulfills the strict requirements for access control and least-privilege principles. For monitoring, a SIEM solution provides the centralized log management needed to detect and respond to events in real-time. These aren't just tools; they're the functional components of a compliant ISMS.
Risk Assessment: The Heart of ISO 27001
Effective risk management has evolved. You can't rely on subjective guessing anymore. Modern ISMS frameworks use data-driven risk identification. This means defining your Risk Treatment Plan (RTP) based on actual threat intelligence and system vulnerabilities. Establishing measurable Key Performance Indicators (KPIs) allows you to track security performance over time. This transparency builds confidence with stakeholders and ensures your certification remains valid through surveillance audits. If you want to ensure your technical controls match your compliance goals, it's worth exploring how OAD Technologies bridges this gap.
Choosing ISO 27001 Certification Consultants in the UAE
Not all iso 27001 certification consultants uae offer the same level of depth. Many firms operate as generalist management consultants, treating information security with the same broad strokes they'd use for ISO 9001 quality standards. This approach is increasingly dangerous in 2026. A generalist might help you write a policy, but they often lack the engineering expertise to help you enforce it. You need a cybersecurity-first GRC partner who acts as a master designer of systems, bridging the gap between high-level governance and the actual configuration of your digital environment.
Local presence in the UAE is another critical factor. The regional threat landscape is distinct, with specific attack vectors targeting the Emirates' financial and energy sectors. A consultant who understands the local regulatory pulse ensures your ISMS isn't just a generic template but a customized shield. Avoid "certification-in-a-box" solutions. These rigid, standardized manuals usually fail under the scrutiny of a rigorous audit because they don't reflect how your business actually operates. Real compliance requires a proactive, solution-oriented mindset that values long-term resilience over a quick, superficial fix.
Criteria for Evaluating a GRC Partner
Technical verification is the first step in your evaluation. Ask potential consultants if they can integrate advanced security operations, such as Managed Detection and Response (MDR), into your compliance framework. Your partner should demonstrate a proven track record in highly regulated UAE industries like healthcare, finance, or government-linked entities. They must also have the capacity to provide post-certification support. ISO 27001 is a journey of continuous improvement, not a destination. A partner who provides ongoing monitoring and support ensures your security posture evolves alongside emerging threats.
The Pitfalls of Paper-Only Compliance
Paper-only compliance creates a false sense of security that evaporates during a technical audit. If your documentation says you have robust access controls but you can't provide system logs to prove it, auditors will issue a major non-conformity. There's also a significant hidden cost to implementing "standard" policies that don't align with your workflow. These generic rules often create operational friction, forcing your team to work around the system rather than with it. Technical validation is the only way to ensure long-term ISO 27001 viability. By choosing iso 27001 certification consultants uae who prioritize technical evidence, you ensure your investment yields a truly secure and compliant enterprise.
The 5-Phase Roadmap to Achieving ISO 27001 Certification
Achieving ISO 27001 certification isn't a linear paperwork trail; it's a rigorous engineering lifecycle. Navigating this journey requires iso 27001 certification consultants uae who understand that every technical control must produce verifiable evidence. A structured roadmap ensures that your Information Security Management System (ISMS) is both compliant and operationally sound. This process transforms your security posture from a set of abstract goals into a defensible, high-performance architecture.
Phase 1 & 2: Building the Foundation
The first steps involve defining the context of your organization and identifying interested party requirements. This stage is critical for setting the boundaries of your ISMS. Without a clear scope, you risk inflating costs through unnecessary complexity. We conduct a comprehensive technical gap analysis against all 93 controls of the ISO/IEC 27001:2022 standard. This analysis provides a data-driven baseline of your current security maturity. From here, we develop a realistic timeline for certification, ensuring your team has a clear path to follow without disrupting daily business operations.
Phase 3 & 4: Remediation and Validation
The most effective iso 27001 certification consultants uae prioritize Phase 3, where the actual remediation happens. This is the "doing" phase. You'll close technical gaps through infrastructure hardening and the deployment of specific security solutions. This includes implementing Data Loss Prevention (DLP) to safeguard sensitive data and Identity and Access Management (IAM) to enforce strict access controls. We also integrate Endpoint Detection and Response (EDR) to fulfill monitoring requirements.
Validation follows remediation. We train your employees to ensure information security awareness is deeply embedded in your corporate culture. Before the external registrar arrives, we conduct a mandatory internal audit. This stress-test identifies potential non-conformities, allowing us to correct them in a controlled environment. If you're ready to move beyond templates and build a technically sound ISMS, partner with OAD Technologies for your certification journey.
Phase 5: Certification Audit
The final phase is the external audit, conducted in two stages. Stage 1 is a documentation review where the auditor verifies that your ISMS framework meets the standard's requirements. Stage 2 is the evidence-based implementation audit. Here, the auditor looks for proof that your controls, such as SIEM logs or VAPT reports, are functioning as described. By following our technical-first roadmap, you can navigate both stages with confidence, knowing your system is built on engineering excellence rather than just policy manuals.
OAD Technologies: Bridging Technical Security and GRC in the UAE
OAD Technologies approaches compliance from a rigorous engineering perspective. We aren't just advisors who hand over a stack of templates; we're master designers of resilient digital systems. While many iso 27001 certification consultants uae focus strictly on the audit date, we focus on the security architecture that outlasts the audit. Our philosophy centers on security-driven compliance. We ensure every policy in your ISMS is backed by a technical control that actually protects your business assets from real-world threats.
We solve the "evidence gap" by integrating our technical security operations directly into your GRC framework. Our Managed Detection and Response (MDR) and SIEM solutions provide the continuous, real-time monitoring required by the ISO/IEC 27001:2022 standard. Instead of scrambling for logs during an audit, you'll have a system that generates compliance evidence automatically. Our UAE-based consultants possess the unique ability to translate complex technical risks for executive leadership while providing deep configuration guidance for your engineering teams.
A Master Designer of Integrated Systems
We reject the standardized, one-size-fits-all approach to information security. Your business objectives and existing tech stack define the boundaries of our strategy. We build customized ISMS frameworks that create a perfect synergy between human insight and technological capacity. This proactive mindset ensures your compliance efforts don't create operational friction. Instead, they enhance your enterprise resilience through:
- Customized Control Mapping: Aligning your specific network architecture with Annex A requirements.
- Engineering-Led Remediation: Hardening your infrastructure based on rigorous VAPT results.
- Long-Term Viability: Building systems that adapt to the evolving UAE regulatory environment and emerging global threats.
Next Steps: Your Journey to ISO 27001
Your path to certification begins with a clear understanding of where you stand. We start by assessing your current maturity level and identifying the specific compliance needs of your industry. From there, we develop a strategic roadmap that doesn't just aim for a certificate but actively improves your overall security posture. We guide you through every technical implementation, from Identity and Access Management (IAM) to Data Loss Prevention (DLP), ensuring your organization is ready for the scrutiny of 2026's regulatory climate.
Future-Proofing Your Compliance Architecture
The transition to ISO/IEC 27001:2022 represents a fundamental shift toward technical accountability. By prioritizing actual enforcement over static policy manuals, your organization builds a resilient Information Security Management System that withstands both audits and real-world breaches. Successful implementation in 2026 requires more than a checklist; it demands a deep integration of security operations with governance standards. This alignment ensures you meet the strict mandates of the UAE PDPL and ISR while maintaining operational agility.
Partnering with specialized iso 27001 certification consultants uae allows you to bridge the gap between regulatory requirements and technical reality. Our team provides expert UAE-based GRC consultancy backed by integrated MDR and SIEM solutions for continuous compliance monitoring. We bring deep experience in regional alignment to ensure your certification journey is efficient and strategically sound. This technical-first approach transforms compliance from a burden into a powerful driver of business trust and digital growth.
Secure your enterprise's future with ISO 27001 certification consultancy from OAD Technologies. Your path to technical excellence and verified compliance starts with a single, decisive step toward better security.
Frequently Asked Questions
How long does it typically take to achieve ISO 27001 certification in the UAE?
The certification process generally takes between six to twelve months depending on your organization's size and current security maturity. Smaller firms with fewer complex systems might reach readiness in six months, while large enterprises often require a full year to implement and test all 93 controls. This timeline includes the initial gap analysis, risk treatment, and the mandatory internal audit phase before the final registrar assessment.
What is the difference between ISO 27001:2013 and the new ISO 27001:2022 standard?
The 2022 update streamlined the control set from 114 to 93 and introduced a new four-theme structure: Organizational, People, Physical, and Technological. It added 11 new controls specifically designed to address modern threats like cloud service security and data masking. Organizations had until October 31, 2025, to transition, meaning all audits in 2026 now focus exclusively on the 2022 requirements.
Can we achieve ISO 27001 certification without external consultants?
While it's possible to manage the process internally, most organizations find the technical mapping and documentation requirements overwhelming without specialized help. Engaging iso 27001 certification consultants uae ensures that your technical controls, such as SIEM and IAM, align perfectly with the auditor's expectations. Professional guidance helps you avoid common implementation errors that lead to major non-conformities and delayed certification.
How does ISO 27001 help with UAE Personal Data Protection Law (PDPL) compliance?
ISO 27001 serves as the operational framework for meeting the strict security mandates of the UAE PDPL. The standard's focus on risk assessment and data protection directly supports the law's requirements for technical and organizational measures to safeguard personal data. Implementing these controls helps you manage the 72-hour breach notification period and other regulatory obligations defined by the UAE Data Office.
What are the common reasons for failing an ISO 27001 certification audit?
Failure most often stems from a lack of technical evidence or inconsistent control enforcement. Auditors frequently identify major non-conformities when a company has the correct policies on paper but cannot provide system logs or VAPT reports to prove those policies are active. Inadequate risk assessments and a failure to demonstrate continuous improvement during the management review also lead to unsuccessful audits.
What is the role of the Statement of Applicability (SoA) in the certification process?
The SoA is the most critical document in your ISMS because it identifies which of the 93 ISO 27001 controls you've implemented and why. It provides a clear summary of your security perimeter and justifies any exclusions based on your specific business context. Auditors use the SoA as their primary roadmap to verify that you've addressed all relevant risks within your defined scope.
How much does ISO 27001 certification cost for a UAE-based enterprise?
Total investment depends on your organization's complexity, the number of sites in scope, and the current state of your technical infrastructure. Costs typically include professional consultancy fees, internal audit program expenses, and the fees charged by the accredited certification body. For an accurate estimate, iso 27001 certification consultants uae should evaluate your specific environment and remediation needs before providing a customized quote.
How often do we need to undergo re-certification or surveillance audits?
The ISO 27001 certificate is valid for a three-year cycle. During this period, you must undergo annual surveillance audits in the first and second years to ensure your ISMS remains effective and compliant. In the third year, a full re-certification audit is required to renew the certificate for another three-year term, confirming that your security posture has evolved with new threats.
Disclaimer
Content by OAD Technologies is for general informational purposes only and does not constitute professional or cybersecurity advice. No warranties are made regarding accuracy or completeness; reliance is at your own risk. OAD Technologies shall not be liable for any direct or indirect losses arising from use of this content.


