In 2026, a single unpatched vulnerability isn't just a technical oversight; it's a potential AED 1 billion liability under CBUAE Decree-Law No. 6 of 2025. You likely recognize the inherent risk in the security gap that forms between your annual audits, especially as rapid software release cycles outpace traditional testing schedules. Relying on a snapshot of your security from six months ago leaves your digital assets exposed to modern zero-day threats that don't wait for your next scheduled window. Understanding the strategic benefits of continuous vapt is now essential for any UAE enterprise aiming to maintain its license to operate and its reputation for reliability.
This article demonstrates how shifting from periodic audits to continuous vulnerability assessment and penetration testing (VAPT) secures your infrastructure against evolving 2026 threats. We'll show you how to move beyond compliance fatigue and streamline your reporting for the National Cyber Accreditation Programme (NCAP). By the end of this guide, you'll understand how persistent validation reduces risk while aligning your security investments with your broader business growth objectives. This transition ensures your organization remains resilient, even as the regulatory and threat landscapes continue to shift.
Key Takeaways
- Understand why periodic testing creates a "Snapshot Fallacy" that leaves your infrastructure vulnerable to threats that emerge between annual audits.
- Learn how the integration of automated discovery and human expertise provides persistent visibility into your evolving digital attack surface.
- Discover the strategic benefits of continuous vapt in reducing zero-day exploitation risks while relieving remediation pressure on internal IT teams.
- See how persistent testing simplifies compliance with the UAE’s evolving IA regulations, NESA standards, and the Personal Data Protection Law.
- Explore how to transition from traditional security vendors to a strategic partnership that prioritizes long-term digital relevance and resilience.
The Evolution of Vulnerability Management: Why Periodic Testing Fails in 2026
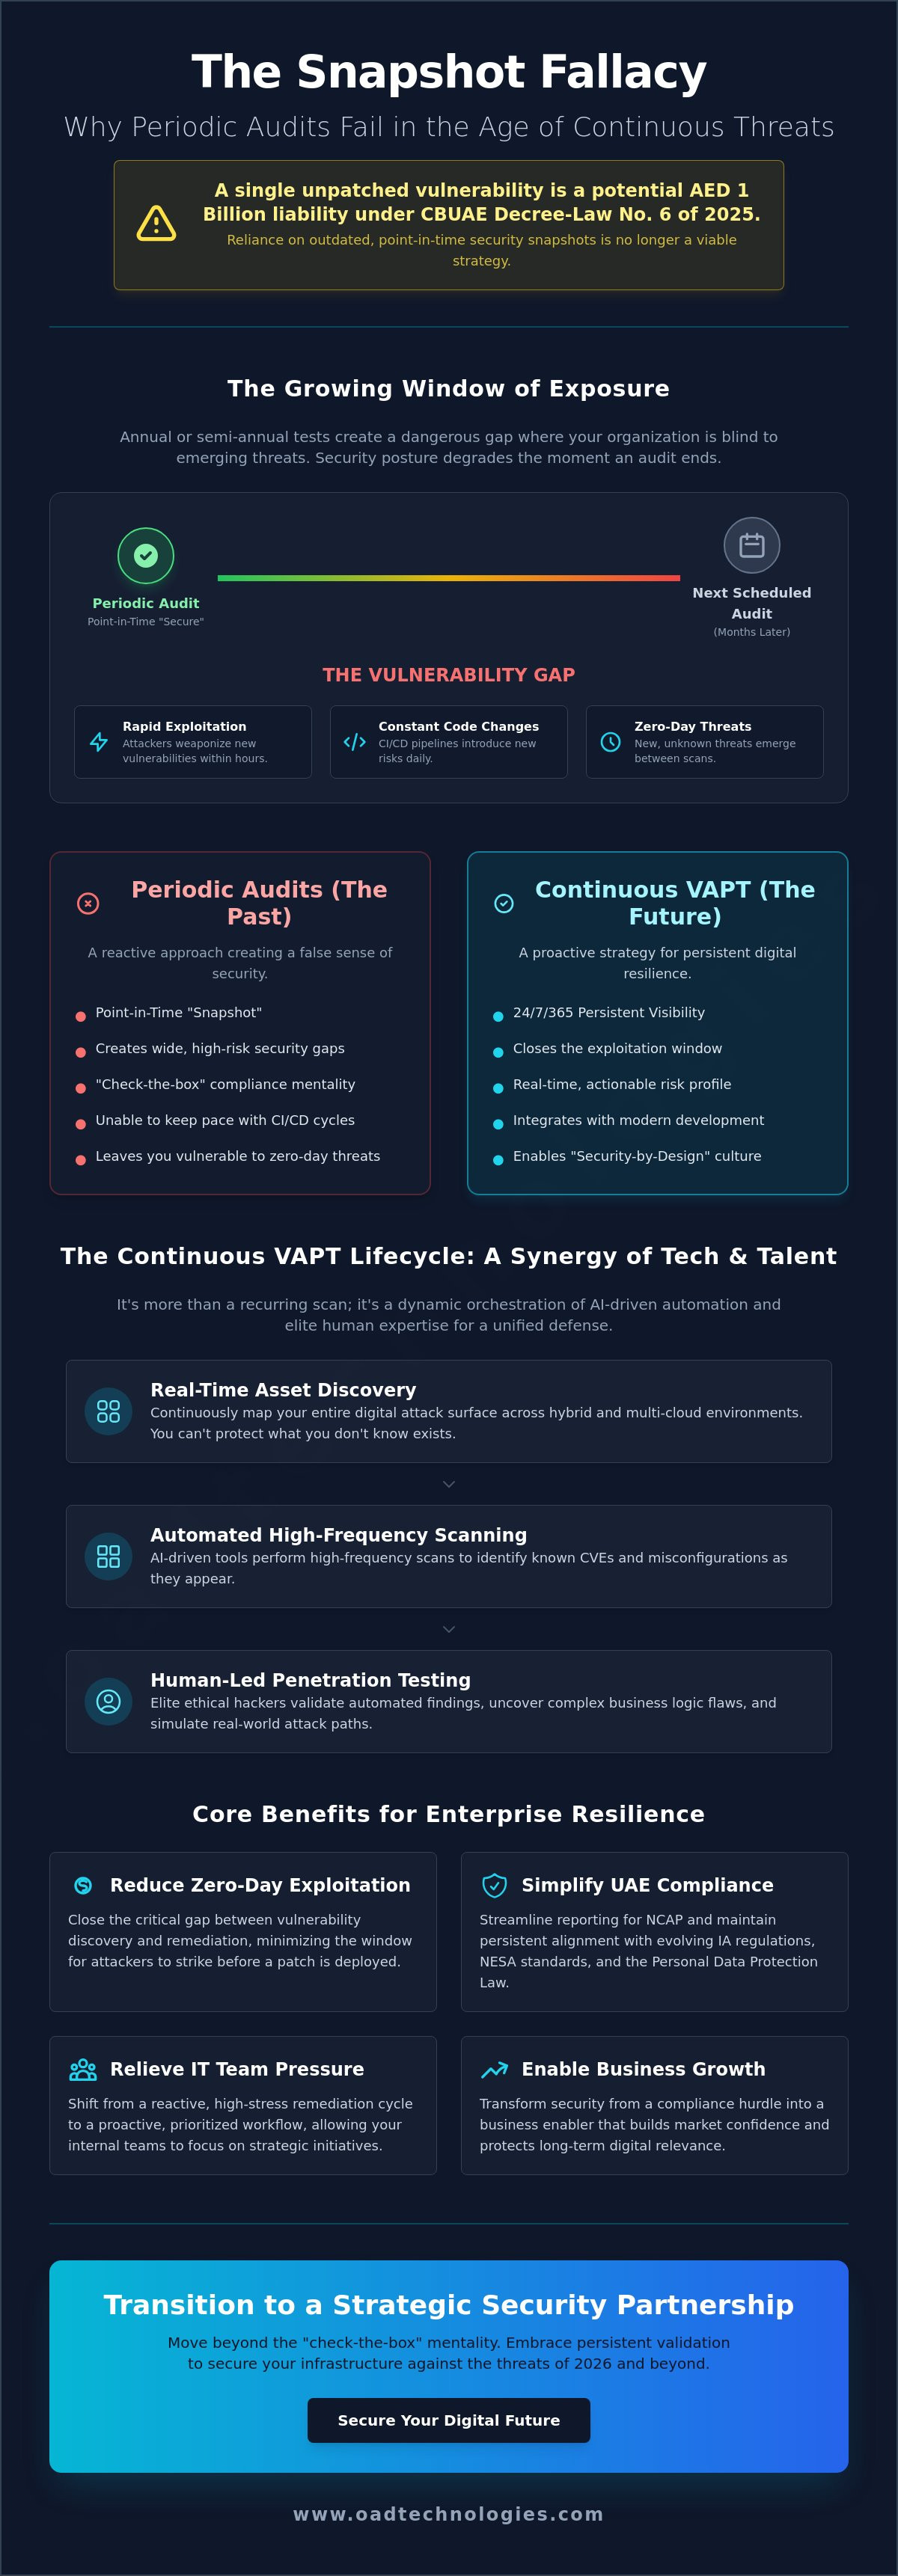
The cybersecurity environment in 2026 has reached a level of complexity where traditional, point-in-time assessments no longer provide adequate protection. With thousands of new Common Vulnerabilities and Exposures (CVEs) documented every month, the "Snapshot Fallacy" represents a dangerous misunderstanding of digital risk. This fallacy suggests that a clean audit report today guarantees safety tomorrow. In reality, your security posture begins to degrade the moment a test concludes. Relying on reactive measures is a costly gamble; a single unaddressed vulnerability can lead to catastrophic data loss or operational downtime. Transitioning to a model that emphasizes the benefits of continuous vapt allows your organization to shift from a static compliance posture to a state of persistent resilience.
Effective penetration testing serves as the backbone of this strategy, but its value is severely diminished when performed only once or twice a year. Modern enterprises require a proactive architecture that identifies exposures as they arise, rather than months after they've been weaponized by threat actors. By adopting a continuous model, you ensure that your defense mechanisms evolve at the same speed as the threats they are designed to stop.
The Shrinking Window of Exploitation
Attackers now weaponize new vulnerabilities within hours of their public disclosure. This rapid turnaround makes the interval between annual or semi-annual tests an unacceptable risk window for any enterprise. Your development teams likely use rapid CI/CD pipelines to push code updates daily, if not hourly. These constant changes to your software architecture mean that your attack surface is in a state of perpetual flux. Traditional security audit cycles simply can't keep pace with this level of agility. One of the primary benefits of continuous vapt is its ability to integrate with these development lifecycles, ensuring that new code doesn't introduce critical weaknesses that remain undetected for months. It's about closing the gap between discovery and remediation before an adversary can capitalize on it.
Moving Beyond the "Check-the-Box" Compliance Mentality
A "check-the-box" approach to compliance often creates a false sense of security among executive leadership. While a periodic VAPT report might satisfy a regulatory requirement on paper, it doesn't reflect the actual, real-time risk profile of the business. Organizations are now shifting toward "Security-by-Design," where persistent monitoring and validation become part of the core operational DNA. This transition bridges the gap between technical findings and strategic business goals. Instead of viewing security as a hurdle to overcome, forward-thinking leaders treat it as a foundational element that enables safe, rapid expansion and protects long-term digital relevance. It's a move from mere survival to strategic market confidence.
What is Continuous VAPT? A Synergy of Automation and Human Intelligence
Continuous VAPT isn't just a recurring scan; it's a dynamic orchestration of advanced technology and elite human insight. While many organizations rely on basic vulnerability scanning, these tools often fail to see the larger picture. They identify isolated flaws but miss the complex paths an attacker might take to compromise a network. By combining AI-driven discovery with manual penetration testing, enterprises gain 24 X 7 visibility into their security posture. This synergy ensures that your defenses don't just exist on paper but are actively tested against real-world scenarios. It's this integration with the broader ecosystem, including your SIEM and EDR solutions, that provides a unified front against sophisticated adversaries. One of the primary benefits of continuous vapt is the ability to maintain this high-fidelity view of your risks without the manual overhead of scheduling individual tests.
The Continuous VAPT Lifecycle
The process begins with real-time asset mapping across hybrid and multi-cloud environments. You can't protect what you don't know exists, and in 2026, shadow IT and ephemeral cloud instances make discovery a constant challenge. Once the attack surface is defined, high-frequency scanning identifies known flaws and misconfigurations. This systematic approach aligns with the industry best practices outlined in CIS Critical Security Control 7, which emphasizes the need for continuous monitoring to reduce the window of opportunity for attackers. However, the true value lies in the validation phase. Here, targeted manual testing determines whether a vulnerability is actually exploitable. This step is crucial for eliminating the noise of false positives and proving the potential impact on your business operations, allowing your team to focus on the most critical threats first.
Human-Led Validation in an Automated World
While algorithms are excellent at identifying patterns, they struggle with the creative leaps required to exploit modern systems. One of the core benefits of continuous vapt is that it places human intelligence at the center of the process. A machine follows a script; a professional tester thinks laterally. They chain minor vulnerabilities together to achieve a major breach, mimicking the behavior of a sophisticated threat actor. This human oversight transforms a list of technical bugs into a prioritized roadmap for remediation. At OAD Technologies, we act as a strategic architect for your defense, ensuring that every finding is context-aware and actionable. Our approach moves beyond generic reports to provide customized solutions for complex infrastructures. If you're looking to strengthen your resilience, exploring a tailored vulnerability assessment and penetration testing strategy is the next logical step to secure your long-term digital relevance.
Core Benefits of Continuous VAPT for Enterprise Resilience
The shift toward persistent testing represents a fundamental change in how enterprises perceive digital risk. One of the primary benefits of continuous vapt is the direct translation of technical security activities into measurable business value. While traditional audits often feel like a periodic hurdle, a continuous model creates a stable environment for strategic expansion. By identifying critical exposures in real-time, organizations avoid the catastrophic financial impact of a successful breach, which in 2026 can involve massive regulatory fines and irreparable brand damage. This approach aligns perfectly with the principles found in the OWASP Vulnerability Management Guide, which advocates for a structured, lifecycle-based approach to handling flaws.
Integrating this model into your broader strategy ensures that vulnerability assessment and penetration testing (VAPT) is no longer a siloed IT task. Instead, it becomes a core component of your operational resilience. This alignment allows leadership to make informed decisions based on live data rather than outdated reports from previous quarters. Beyond just finding bugs, this persistent validation builds customer trust. In a digital-first economy, your clients need to know that their data is protected by a system that never sleeps, rather than one that is only checked once a year.
Closing the Window of Exposure
Continuous monitoring allows enterprises to identify zero-day threats before adversaries can weaponize them. This is particularly vital for maintaining a strong cloud security posture, where misconfigurations can expose sensitive data in seconds. By linking rapid detection to a Managed Detection and Response (MDR) framework, you create a closed-loop system where vulnerabilities are not just found but actively mitigated. This synergy reduces the time-to-remediation, effectively closing the window of exposure that attackers rely on. It ensures that your defense is always one step ahead of the evolving threat landscape.
Optimizing Security ROI and Resource Allocation
One of the most tangible benefits of continuous vapt is the optimization of internal resources. IT teams often suffer from alert fatigue caused by an unprioritized list of vulnerabilities. A continuous, expert-validated model moves the organization from reactive firefighting to a structured remediation workflow. By providing data-driven insights, it empowers your team to focus on the small percentage of flaws that represent the highest actual risk to the business. This precision ensures that security spending is directed toward the most impactful areas, maximizing your return on investment while supporting long-term strategic goals. It turns your security department into a proactive partner in business growth rather than a cost center.
Navigating UAE Regulatory Compliance with Persistent Testing
Compliance in the United Arab Emirates has transitioned from a voluntary best-practice model to a rigorous, evidence-based operational requirement. With the implementation of CBUAE Decree-Law No. 6 of 2025, digital banks and fintech organizations face mandatory cybersecurity controls that demand more than just an annual checkmark. The potential penalties for non-compliance, which can reach AED 1 billion, underscore the necessity of a more robust approach. One of the strategic benefits of continuous vapt is its ability to provide a constant stream of audit-ready data that satisfies the UAE Cybersecurity Council’s framework. By maintaining a state of persistent validation, enterprises can demonstrate their commitment to national security standards without the frantic preparation typically associated with periodic audits.
This proactive stance is a critical component of modern Governance Risk and Compliance (GRC) strategies. It transforms technical findings into strategic assets that support licensing, investor confidence, and long-term partnerships. For UAE enterprises, staying ahead of regulatory scrutiny means moving beyond reactive fixes and adopting a system that identifies gaps before they become liabilities. This approach ensures that your organization doesn't just meet the baseline but actively shapes a resilient digital future in the region.
Meeting ISR and NESA Requirements
Static audits often fall short of the rigorous demands set by the National Electronic Security Authority (NESA) and the Information Security Regulation (ISR). These standards require ongoing vigilance rather than a single point-in-time assessment. Continuous VAPT acts as a proactive evidence-gathering tool, allowing compliance officers to present a real-time view of the organization's security posture. By integrating these technical assessments with Identity and Access Management (IAM) audits, businesses can ensure that only authorized personnel have access to critical systems, further aligning with the National Cyber Accreditation Programme (NCAP) mandates for 2026. This level of integration is essential for organizations handling Critical Information Infrastructure (CII).
Data Sovereignty and the UAE PDPL
The UAE Personal Data Protection Law (PDPL) mandates that technical safeguards are in place to protect sensitive corporate and consumer assets. Persistent testing is the most effective way to prevent the data leaks that trigger severe PDPL penalties. It ensures that encryption protocols, access controls, and storage configurations are constantly verified against the latest exploitation techniques. As a local partner, OAD Technologies understands the nuances of national regulatory alignment, providing the technical authority needed to navigate these complex legal requirements. If you need to strengthen your regulatory standing, we invite you to explore our specialized Governance, Risk, and Compliance solutions to ensure your enterprise remains compliant and resilient.
OAD Technologies: Your Partner in Persistent Digital Defense
OAD Technologies doesn't operate as a distant third-party vendor. We act as an extension of your own team; a strategic architect of systems dedicated to your long-term digital relevance. In the high-stakes environment of 2026, a standardized approach to security is no longer viable. One of the key benefits of continuous vapt when partnered with OAD is the creation of a bespoke security architecture tailored specifically to the intricate needs of UAE enterprises. We bridge the gap between high-level innovation and practical business results, ensuring that your investment in security translates directly into operational stability and market confidence.
Our methodology focuses on the powerful synergy between human insight and technological capacity. By integrating continuous VAPT with our Managed Detection and Response (MDR) and Security Information and Event Management (SIEM) solutions, we create a unified defense posture. This holistic view allows us to move beyond simply identifying bugs to actively shaping the future of your digital infrastructure. We ensure that every layer of your defense is synchronized, proactive, and capable of withstanding the most sophisticated adversarial logic. This integrated approach provides the visibility needed to manage risk across hybrid environments effectively.
The OAD Advantage: Precision and Craftsmanship
We pride ourselves on a commitment to high-quality engineering and rigorous standards. Unlike platforms that rely solely on automated outputs, OAD prioritizes expert-led validation to ensure every finding is accurate and actionable. This proactive, solution-oriented mindset is backed by engineering excellence that prioritizes long-term success over quick fixes. We understand that technical authority is earned through precision; therefore, our assessments provide the deep intelligence required to navigate complex software architectures and data strategies. It's about providing a roadmap that empowers your people rather than just replacing your processes.
Securing Your Future: Strategic Next Steps
Transitioning your organization from periodic audits to a state of persistent resilience requires a clear and logical roadmap. The process begins by identifying the critical assets that define your competitive edge and mapping them against the current threat landscape. Integrating your testing cycle with Data Loss Prevention (DLP) protocols ensures that your most sensitive information remains shielded even as new vulnerabilities are discovered. This multi-layered approach is one of the essential benefits of continuous vapt, as it prevents the data leaks that lead to regulatory penalties and loss of customer trust. To begin your journey toward persistent digital defense, contact OAD Technologies for a customized technical security assessment that aligns with your strategic business goals.
Securing Your Strategic Digital Advantage in 2026
The transition from periodic audits to a model of persistent validation is no longer optional for enterprises navigating the 2026 threat landscape. By closing the security gap between annual tests, your organization moves beyond the "Snapshot Fallacy" toward a state of genuine, data-driven resilience. We've explored how the benefits of continuous vapt extend far beyond technical remediation; they provide a foundation for regulatory alignment, investor confidence, and sustainable business growth. This shift ensures your defense mechanisms evolve as rapidly as the vulnerabilities they're designed to mitigate.
Choosing a UAE-based strategic cybersecurity partnership allows you to navigate regional mandates with absolute precision. Our approach provides expert-led validation of all automated findings, ensuring your team focuses on actionable intelligence rather than technical noise. With seamless integration into MDR and GRC frameworks, we help you maintain a unified front against sophisticated adversaries. Secure your enterprise with OAD Technologies’ Continuous VAPT solutions today. Building a resilient future starts with a proactive mindset and a commitment to your ongoing digital relevance.
Frequently Asked Questions
How does continuous VAPT differ from a standard automated vulnerability scan?
Continuous VAPT goes beyond simple automated scanning by integrating ongoing manual penetration testing to identify complex, multi-stage exploit chains. While a standard scan only looks for known signatures of common flaws, a continuous model uses human intelligence to validate findings and uncover logical vulnerabilities that machines often miss. This comprehensive approach ensures that your security posture is tested against the same creative tactics used by modern threat actors.
Will continuous testing impact the performance of our production environment?
No, the testing process is carefully engineered to be non-intrusive and uses throttled scanning techniques to ensure zero impact on your operational performance. We tailor the testing cadence to your specific infrastructure capacity and can schedule more intensive assessments during off-peak hours. This allows you to maintain high-fidelity visibility into your risks without risking the stability of your critical business applications or customer-facing services.
How often does the "continuous" cycle actually run?
The cycle is persistent, with automated asset discovery and vulnerability identification running daily or in real-time as your infrastructure evolves. These automated layers are supplemented by regular, deep-dive manual assessments conducted by expert testers whenever significant changes occur in your environment. One of the primary benefits of continuous vapt is this ability to detect and validate new exposures within hours of their emergence rather than waiting for an annual audit window.
Can continuous VAPT help us meet UAE ISR and NESA compliance requirements?
Yes, it is specifically designed to provide the evidence-based, persistent monitoring required by the UAE’s latest national security frameworks. Since the UAE Cybersecurity Council and NESA now prioritize continuous validation over periodic reviews, this model ensures you always have audit-ready documentation. It simplifies the path to NCAP accreditation by providing a transparent, real-time record of your organization's risk management and remediation activities.
How does continuous testing integrate with our existing SIEM and SOC operations?
The system integrates seamlessly with your existing security stack via API or native connectors, feeding validated findings directly into your SIEM or SOC dashboard. This integration allows your incident response teams to focus their energy on confirmed, exploitable vulnerabilities rather than sifting through unverified alerts. By enriching your SOC data with high-fidelity vulnerability intelligence, you improve your overall detection and response capabilities across the entire enterprise.
What is the role of human penetration testers in an automated continuous testing model?
Human testers provide the creative logic and lateral thinking required to chain together minor vulnerabilities into a significant breach scenario. While automation handles the repetitive task of identifying known flaws, our experts validate those findings to eliminate false positives and conduct targeted manual exploits. This human-led approach ensures that every report you receive is actionable, context-aware, and reflects the true risk to your specific business operations.
Is continuous VAPT suitable for small and medium enterprises, or only large corporations?
It is highly beneficial for organizations of all sizes, especially as threat actors increasingly target SMEs with sophisticated attacks. While large enterprises use it to manage vast, complex architectures, smaller organizations benefit from the expert-managed nature of the service. It essentially acts as a force multiplier for smaller IT teams, providing them with the same level of technical authority and protection as a large-scale internal security department.
How does OAD Technologies ensure that continuous testing doesn't lead to alert fatigue?
We eliminate alert fatigue by providing only expert-validated, prioritized remediation roadmaps rather than raw data dumps. Every finding is reviewed by our technical specialists to confirm its exploitability and potential impact on your business before it reaches your desk. This ensures that your internal teams spend their time fixing the small percentage of vulnerabilities that represent the highest actual risk, leading to much more efficient resource allocation.
Disclaimer
Content by OAD Technologies is for general informational purposes only and does not constitute professional or cybersecurity advice. No warranties are made regarding accuracy or completeness; reliance is at your own risk. OAD Technologies shall not be liable for any direct or indirect losses arising from use of this content.