
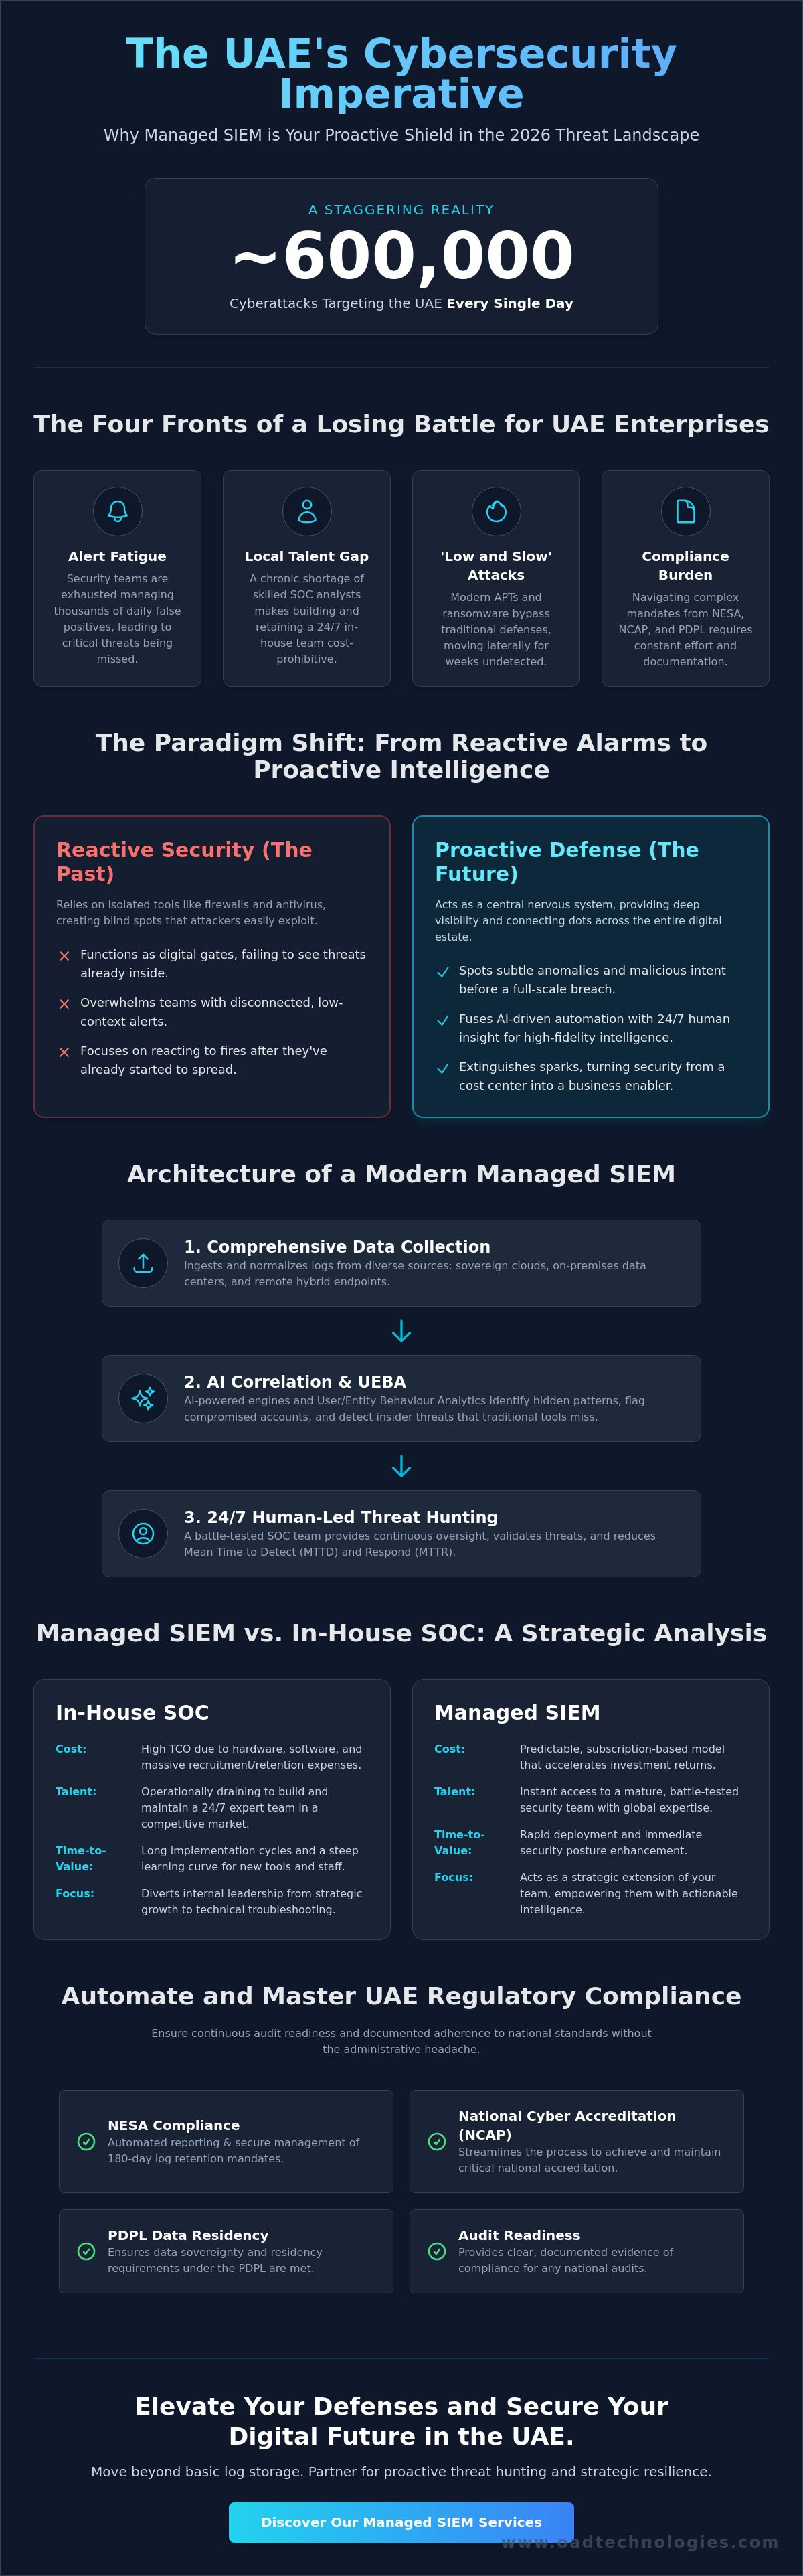
With nearly 600,000 cyberattacks targeting the UAE every single day in 2026, your security team isn't just fighting hackers; they're fighting a losing battle against alert fatigue. You've likely felt the strain of trying to source local cybersecurity talent while keeping up with NESA's 180-day log retention mandates and the National Cyber Accreditation Programme (NCAP). It's exhausting to manage thousands of false positives when you're also trying to ensure data residency compliance under the PDPL. This is why managed siem services uae have evolved from simple log storage into a vital strategic partnership.
We understand that you need more than just software; you need a system that works as hard as your business does. This guide explains how you can achieve 24 X 7 threat visibility and documented compliance for national audits without hiring a full internal SOC team. We'll preview how modern SIEM architectures reduce Mean Time to Detect (MTTD) and Respond (MTTR) by fusing AI-driven automation with human insight. Discover how to turn your security operations from a reactive cost center into a proactive shield for your digital growth and long-term resilience.
Key Takeaways
- Learn why shifting from basic log storage to proactive threat hunting is essential for maintaining digital resilience in the UAE's high-pressure security environment.
- Understand how AI-driven correlation engines analyze data across hybrid infrastructures to isolate genuine threats and eliminate operational noise.
- Analyze the strategic cost-benefit of managed siem services uae versus building an in-house SOC, focusing on accelerated time-to-value and investment returns.
- Discover how to automate complex regulatory reporting to meet NESA and Information Assurance Standards while ensuring continuous audit readiness.
- Explore how a bespoke SIEM architecture integrates human expertise with advanced technology to safeguard your organization's long-term digital relevance.
What are Managed SIEM Services and Why are They Critical for UAE Enterprises?
Managed SIEM is a high-performance security model that fuses advanced technology with 24 X 7 human oversight. While Security Information and Event Management (SIEM) historically focused on aggregating logs for compliance, today's managed siem services uae act as the central nervous system of a modern Security Operations Center (SOC). This evolution shifts the focus from passive record-keeping to aggressive, proactive threat hunting. In the 2026 landscape, where UAE entities face nearly 600,000 daily cyberattacks, having a central 'brain' to correlate data across the entire digital estate is no longer optional. Sophisticated Advanced Persistent Threats (APTs) and targeted ransomware require a system that doesn't just see data but understands the context behind every event.
The Shift from Reactive to Proactive Defense
Traditional defenses like firewalls and antivirus software function as digital gates, but they often fail to detect attackers who have already bypassed the perimeter. Modern adversaries use 'low and slow' tactics, moving laterally through a network over weeks or months to avoid detection. Managed SIEM provides the deep visibility required to spot these subtle anomalies. By ingesting telemetry from cloud environments, on-premises servers, and remote endpoints, it builds a holistic security posture that identifies malicious intent before it escalates into a full-scale breach. This visibility ensures that security teams aren't just reacting to fires but extinguishing sparks before they spread. Relying on isolated tools creates blind spots that attackers are eager to exploit; SIEM closes those gaps by connecting the dots between seemingly unrelated activities.
Addressing the UAE Cybersecurity Talent Gap
Organizations across Dubai and Abu Dhabi face a persistent challenge: the chronic shortage of skilled SOC analysts capable of managing complex security architectures. Recruiting and retaining a 24 X 7 internal team is both cost-prohibitive and operationally draining for most enterprises. Choosing managed siem services uae provides instant access to a mature, battle-tested security team without the overhead of local recruitment cycles. This model allows businesses to leverage global expertise while maintaining a focus on local operational goals. It eliminates the burden of training staff on rapidly changing toolsets, allowing your internal leadership to focus on strategic growth rather than technical troubleshooting. Managed SIEM functions as a strategic extension of your internal IT team, empowering your people with high-fidelity intelligence rather than overwhelming them with manual log analysis.
The Architecture of Modern SIEM: Beyond Simple Log Aggregation
Modern managed siem services uae rely on a multi-layered architecture designed to process massive volumes of telemetry in real time. This process begins with comprehensive data collection, ingesting logs from diverse sources including sovereign cloud regions, on-premises data centers, and remote hybrid endpoints. It's not just about storage; it's about normalization and enrichment. By aligning with NIST cybersecurity guidelines, these systems ensure that every data point contributes to a larger security narrative. This structured approach allows organizations to maintain visibility across complex, fragmented infrastructures that are common in the UAE's digital-first economy.
Correlation engines represent the next layer of sophistication. These engines use AI to identify patterns across seemingly unrelated events, such as a failed login in Abu Dhabi followed by an unusual database export from a different region. When paired with User and Entity Behaviour Analytics (UEBA), the system moves beyond signature-based detection. It learns the "normal" behavior of your employees and systems, allowing it to flag compromised accounts or potential insider threats that traditional tools would miss. To maximize these insights, many enterprises integrate their SIEM with Managed Detection and Response (MDR) for end-to-end protection. When implementing managed siem services uae, the goal is to create a seamless flow from data ingestion to automated mitigation.
AI and Machine Learning in Threat Detection
AI has transformed SIEM from a noisy alert generator into a high-fidelity intelligence tool. By applying machine learning models that adapt to your specific UAE business environment, the system drastically reduces false positives. This filtering ensures your analysts spend time on critical vulnerabilities rather than chasing ghosts. High-quality threat intelligence feeds further sharpen this detection capability, providing real-time data on known malicious actors and emerging attack vectors specific to the Gulf region. This localized intelligence is vital for staying ahead of regional Advanced Persistent Threats (APTs).
SOAR: Automating the Response
Security Orchestration, Automation, and Response (SOAR) is the logical evolution of the SIEM ecosystem. While a standard SIEM identifies an incident, SOAR automates the containment. It uses pre-defined playbooks to execute repetitive tasks, such as isolating a compromised workstation or revoking a user's access, in seconds. This synergy between detection and automated response is what allows organizations to drastically reduce their Mean Time to Respond (MTTR). For those looking to strengthen their foundational security, integrating these tools with a robust Vulnerability Assessment and Penetration Testing (VAPT) strategy ensures your automated defenses are tuned to your most critical risks.
Managed SIEM vs. In-House SOC: A Strategic Cost-Benefit Analysis
Deciding between building an internal Security Operations Center (SOC) and partnering with a provider for managed siem services uae is a pivotal strategic choice for any maturing enterprise. While an in-house model offers a sense of direct control, the Total Cost of Ownership (TCO) often reveals a different reality. Beyond the heavy initial investment in hardware and software licenses, the ongoing operational burden is substantial. Organizations must account for the infrastructure maintenance and the constant cycle of software updates required to keep the system performant. In contrast, a managed model allows you to bypass these capital hurdles, moving directly to a deployment that delivers results in weeks rather than months.
Time-to-value is perhaps the most critical differentiator in this analysis. An in-house SOC typically requires 12 months or more to reach full operational maturity, including the time spent on procurement, configuration, and team integration. A managed deployment can often go live within 30 days, providing immediate protection against the sophisticated threat landscape of 2026. This speed is complemented by a depth of expertise that is difficult to find in the local market. Partnering with a managed provider gives your business access to specialized threat hunters who analyze global attack patterns daily. These professionals offer a level of insight that generalist IT staff, who are often stretched across multiple roles, simply cannot match.
The Hidden Costs of an In-House SOC
Maintaining a 24 X 7/365 shift rotation is an immense undertaking that many organizations underestimate. To ensure continuous coverage without analyst burnout, a minimum of 8 to 10 dedicated security analysts is usually required. This doesn't just involve salaries; it includes the high cost of continuous training and certifications necessary to combat modern Advanced Persistent Threats (APTs). When you factor in recruitment fees and the high turnover rate in the cybersecurity sector, the financial strain becomes clear. Outsourcing these complexities through managed siem services uae eliminates the need for a massive internal headcount while ensuring your defense remains at the cutting edge of technological innovation.
Operational Advantages of the Managed Model
The shift from unpredictable Capital Expenditure (CAPEX) to a steady, monthly Operational Expenditure (OPEX) model provides significant financial predictability. This allows your leadership to align security spending with business growth. Service Level Agreements (SLAs) further enhance this model by guaranteeing specific detection and response times, creating a framework of accountability. By offloading the relentless task of log monitoring and noise filtering, your internal team is freed to focus on high-level strategic initiatives. This synergy between your core staff and a specialized security partner ensures long-term viability in an increasingly volatile digital market.
Navigating UAE Regulatory Compliance with Managed SIEM
The UAE's regulatory environment has shifted from voluntary best practices to a strict, multi-layered framework of mandatory requirements. For enterprises operating in critical sectors, meeting the National Electronic Security Authority (NESA) standards is a non-negotiable prerequisite for business continuity. Managed siem services uae provide the technical foundation for this compliance by automating the collection and analysis of logs across your entire infrastructure. Rather than manually piecing together reports for an auditor, a managed SIEM provides a centralized repository that demonstrates adherence to Information Assurance (ISR) standards in real time. This level of oversight is essential for government and semi-government entities that must prove they've implemented rigorous security controls.
Federal Decree-Law No. 45 of 2021, the UAE’s Personal Data Protection Law (PDPL), adds another layer of complexity to incident management. Under this law, organizations must adhere to strict notification timelines in the event of a data breach. SIEM technology tracks the exact lifecycle of an incident, providing the forensic evidence needed to satisfy the UAE Data Office (UAEDO). By integrating these capabilities into a broader Governance Risk and Compliance (GRC) strategy, you transform your security data into a strategic asset. This alignment ensures that your technical defenses directly support your legal and operational obligations, protecting your brand from the reputational damage of non-compliance.
Automating Audit Readiness
Audit cycles often cause significant disruption to IT teams, but managed siem services uae mitigate this pressure through pre-built compliance dashboards. These interfaces are specifically mapped to national UAE standards, allowing you to pull comprehensive reports with a few clicks. A critical component of this readiness is the NESA-mandated log retention period, which requires a minimum of 180 days of storage for critical infrastructure organizations. Managed SIEM turns compliance from a manual burden into an automated process. It ensures that every required log is captured, timestamped, and stored securely, making national audits a routine verification rather than a high-stakes crisis.
Data Residency and Sovereign Cloud Considerations
Data residency remains a top priority for UAE enterprises, particularly those handling sensitive national data or financial records. Many regulations require that security logs and sensitive telemetry stay within UAE borders. OAD Technologies supports these local residency requirements by utilizing domestic security operations centers and sovereign cloud regions. By integrating your SIEM with Cloud Security Posture Management (CSPM), you gain a unified view of your local and hybrid cloud environments. This ensures that your data remains compliant with residency laws while benefiting from the scale of modern cloud-native security tools. Strengthen your regulatory posture and ensure long-term viability by exploring our comprehensive GRC solutions today.
OAD Technologies: Elevating UAE Cybersecurity through Managed SIEM Excellence
OAD Technologies doesn't just deploy software; we architect resilience. Our approach to managed siem services uae centers on building bespoke environments that reflect the unique operational realities of Gulf enterprises. We recognize that a one-size-fits-all configuration fails to account for the specific nuances of regional threat actors and the strictness of local data laws. By combining elite human insight with high-performance technology, we ensure that your security operations move beyond simple alerting. Our analysts engage in proactive threat hunting, seeking out the subtle indicators of compromise that automated systems might overlook. This rigorous engineering standard ensures your organization stays ahead of the nearly 600,000 daily cyber threats targeting the region.
Integration is a core pillar of our strategy. A SIEM is only as effective as the data it analyzes, which is why we ensure seamless connectivity with your existing Identity and Access Management (IAM) stack. This allows us to track user lifecycles and detect credential misuse with surgical precision. By bridging the gap between high-level innovation and practical business results, we position your security posture as a driver of long-term viability. We act as a guardian of your digital relevance, ensuring that every integration strengthens the overall system architecture and provides a clear return on your security investment.
A Collaborative Partnership Model
We don't believe in distant vendor relationships. OAD Technologies operates as a strategic extension of your internal team, fostering a culture of transparency and shared responsibility. This partnership includes customized reporting structures designed to speak to both technical specialists and executive leadership. While your IT staff receives granular forensic data, your C-suite gains clear insights into risk mitigation and operational performance. This dual-layered communication ensures that everyone in your organization understands the value of our managed siem services uae. Our commitment is to your long-term digital resilience, helping you navigate the complexities of 2026 and beyond with absolute confidence.
Next Steps for Your Security Evolution
Transitioning to a mature security model is a structured journey. The process begins with a comprehensive technical security assessment where we identify your critical data assets and existing visibility gaps. From there, we establish a clear roadmap for initial log ingestion, eventually scaling to full-scale MDR integration for total environmental protection. This steady, deliberate rhythm ensures that your security matures without overwhelming your operational capacity. Our proactive mindset ensures your roadmap is built on engineering excellence rather than quick fixes. Don't leave your enterprise's future to chance. Secure your enterprise with OAD Technologies' Managed SIEM services today.
Securing Your Digital Future in the Emirates
The transition toward 2026 security operations demands a departure from reactive log management. You've seen how modern architectures integrate AI and SOAR to neutralize threats before they escalate. By choosing managed siem services uae, your organization gains the visibility needed to satisfy NESA and ISR standards while bypassing the immense costs of a 24 X 7 in-house SOC. It's about turning complex telemetry into actionable intelligence that protects your long-term digital viability in a market that faces hundreds of thousands of daily attacks.
OAD Technologies acts as your strategic partner, offering specialized UAE compliance expertise and elite threat hunting tailored for complex environments. We focus on bespoke system integration that empowers your people and secures your growth. Design your strategic security roadmap with OAD Technologies to ensure your enterprise remains resilient against an ever-evolving threat landscape. Your path to a more secure and compliant future starts with a single, decisive step. We're ready to help you navigate this evolution with precision and technical authority.
Frequently Asked Questions
What is the difference between SIEM and a Managed SOC?
SIEM refers to the technical platform that aggregates and correlates security data, while a Managed SOC is the team of experts who monitor and act on that data. Managed siem services uae bridge this gap by providing both the high-performance technology and the human analysis required to interpret complex security events. This ensures that your investment in technology results in actual threat detection rather than just a collection of unread logs.
Can Managed SIEM help our company comply with UAE NESA regulations?
Yes, SIEM is a foundational tool for meeting NESA's Information Assurance Standards and the UAE’s National Electronic Security Authority mandates. It automates the 180-day log retention requirement for critical infrastructure and provides the documented evidence needed for national audits. By centralizing telemetry, you can generate compliance reports that prove your organization follows mandatory security controls without the manual effort of traditional bookkeeping.
How long does it take to deploy a Managed SIEM service in the UAE?
Initial deployment and log ingestion for a managed service typically occur within 30 days. This accelerated timeline allows your business to achieve a mature security posture much faster than building an in-house SOC, which often takes 12 months or more. We focus on a structured roadmap that moves from baseline configuration to advanced threat hunting in a steady, deliberate rhythm that avoids overwhelming your internal resources.
Does Managed SIEM replace my existing security team?
Managed SIEM doesn't replace your IT staff; it empowers them. By offloading the burden of monitoring thousands of daily alerts and false positives, your internal team can focus on high-level business growth and strategic initiatives. Think of it as a strategic extension of your team that provides the 24 X 7 visibility and specialized expertise needed to combat modern Advanced Persistent Threats (APTs) and ransomware.
How does SIEM handle data residency requirements in the UAE?
Data residency is handled by ensuring that all security logs and telemetry are stored within UAE-based data centers or sovereign cloud regions. This approach aligns with Federal Decree-Law No. 45 (PDPL) and other sector-specific mandates that require sensitive data to remain within national borders. We architect the system to ensure your security operations never compromise your legal obligations regarding data sovereignty and residency.
What happens when the SIEM detects a critical threat at 3 AM?
When a critical threat is detected outside of business hours, the system triggers pre-defined SOAR playbooks to provide immediate containment. This might involve automatically isolating a compromised workstation or revoking access to a sensitive database in seconds. Simultaneously, elite security analysts receive a high-priority alert to begin a manual investigation, ensuring the incident is mitigated long before your team starts their workday.
Can OAD Technologies integrate SIEM with our existing cloud environment?
OAD Technologies specializes in integrating SIEM with diverse cloud environments, including AWS, Azure, and Google Cloud. We often pair this with Cloud Security Posture Management (CSPM) to provide a unified view of your hybrid infrastructure. This ensures that your security visibility extends across all cloud-native assets, providing a consistent defense regardless of where your data resides or how your architecture evolves.
Is Managed SIEM suitable for mid-sized UAE businesses or only large enterprises?
Managed siem services uae are highly suitable for both mid-sized businesses and large enterprises. Mid-sized organizations benefit from the predictable OPEX model and instant access to elite security talent without the capital expense of building an internal SOC. Large enterprises leverage the service for its massive scalability and the ability to conduct deep, specialized threat hunting across complex, multi-layered environments that are difficult to manage alone.
Disclaimer
Content by OAD Technologies is for general informational purposes only and does not constitute professional or cybersecurity advice. No warranties are made regarding accuracy or completeness; reliance is at your own risk. OAD Technologies shall not be liable for any direct or indirect losses arising from use of this content.


